Excerpt from TechRadar, Published on October 14, 2026
A major data leak involving AI development company Vibetech has exposed approximately 13.7 million records collected from previous data breaches and cyberattacks. According to TechRadar, the exposed database contained sensitive personal information and account credentials, raising concerns about database security and the protection of previously compromised data.
Sensitive Information Exposed Online
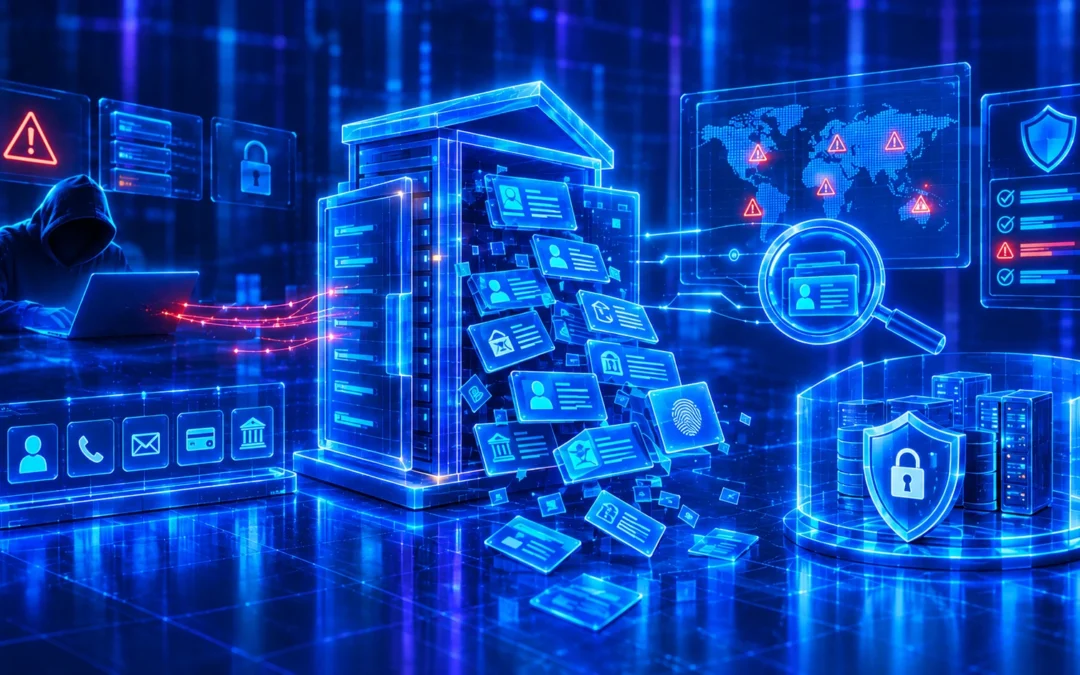
Security researcher Jeremiah Fowler discovered the database accessible online without adequate protection. The records reportedly included names, phone numbers, email addresses, passwords and bank account details belonging to individuals across multiple countries. The archive organized information by company name. Nearly eight million records were associated with AT&T, while other datasets reportedly included information linked to Amazon, Walmart, PayPal and BluBank Digital Bank. The database also contained smaller collections associated with organizations such as the FBI Employee Directory and Interpol. This data leak highlights the risks of combining information from multiple previous incidents into a centralized repository. Even when information originates from older breaches, making it accessible through an unsecured database can create additional opportunities for cybercriminals to exploit exposed credentials and personal details.
Security Risks and Data Protection
Unprotected databases remain a significant cybersecurity concern. Misconfigured cloud storage, weak access controls and inadequate security monitoring can expose sensitive information to unauthorized users. Organizations that collect data for research or development must ensure that appropriate safeguards remain in place throughout the data lifecycle. A data leak involving previously compromised records can also increase the risk of phishing, account takeover and identity fraud. Reused passwords may allow attackers to access other accounts, while exposed contact information can support targeted social engineering attempts. The Vibetech data leak highlights the importance of stronger access controls, continuous security monitoring and responsible data management.
Lessons For Organizations
Organizations should regularly review database configurations, restrict access to authorized personnel and apply encryption where appropriate. They should also monitor storage environments, assess third-party risks and establish procedures for responding to accidental exposure. The incident reinforces the importance of effective data governance and continuous security assessments to prevent sensitive information from becoming publicly accessible.
For more details, read the original report on TechRadar.