
SOC 2 Certification in Chicago
CertPro is a Licensed CPA Firm conducting independent SOC 2 examinations for organizations operating in Chicago, Illinois. All SOC 2 audits are performed under AICPA attestation standards and evaluated against the Trust Services Criteria — covering Security, Availability, Processing Integrity, Confidentiality, and Privacy. SOC 2 attestation reports are issued for both Type 1 and Type 2 engagements, giving Chicago businesses the independent verification their customers and partners require.
OUR CLIENTS










What Is SOC 2 Certification in Chicago?
SOC 2 Certification in Chicago is a formal attestation issued exclusively by a Licensed CPA Firm following an independent examination conducted under AICPA AT-C Section 205 attestation standards. The examination evaluates whether an organization’s internal controls satisfy the Trust Services Criteria established by the American Institute of Certified Public Accountants. The resulting SOC 2 attestation report provides customers, business partners, and stakeholders with independent assurance that an organization’s systems and controls operate as described and meet defined security and operational standards.
Chicago organizations pursuing SOC 2 Certification operate within one of the most concentrated business ecosystems in the United States. The city is home to major financial institutions, SaaS providers, healthcare technology firms, insurance companies, logistics technology businesses, fintech companies, managed service providers, AI startups, cloud service providers, and multinational enterprises. Each of these sectors faces growing customer and regulatory demand for independent verification of data security practices — making SOC 2 Certification in Chicago a critical business requirement rather than an optional differentiator.
The AICPA Trust Services Criteria Framework
The AICPA Trust Services Criteria (TSC) define the control categories against which SOC 2 examinations are conducted. The TSC replaced the previous Trust Services Principles framework and introduced a more structured, criteria-based approach to evaluating service organization controls. Organizations subject to a SOC 2 audit are evaluated against criteria organized under five categories: Security (CC), Availability (A), Processing Integrity (PI), Confidentiality (C), and Privacy (P). Security is the only mandatory category; the remaining four are included based on the organization’s service commitments and contractual obligations to its customers.
Each Trust Services Criteria category contains specific point-of-focus requirements and control activities that auditors evaluate during a SOC 2 examination. The Security category — also known as the Common Criteria — encompasses logical and physical access controls, system operations, change management, risk mitigation, and monitoring activities. Chicago-based technology companies, cloud providers, and financial services organizations typically include multiple TSC categories in their SOC 2 scope to address the full range of customer expectations and contractual commitments related to data protection and system reliability.
SOC 2 Defined: Attestation vs. Certification
The term SOC 2 Certification is widely used in the marketplace, but the technically accurate designation is SOC 2 attestation. Under AICPA standards, a CPA firm issues an attestation report rather than a certificate. This distinction matters: only a Licensed CPA Firm holding the appropriate accreditation and independence qualifications can conduct a SOC 2 examination and issue a valid SOC 2 attestation report. Consulting firms, technology vendors, and advisory organizations cannot issue SOC 2 reports — regardless of the preparation services they provide to help an organization get ready for an audit.
SOC 2 compliance refers to an organization’s internal adherence to the policies, procedures, and controls that align with the Trust Services Criteria. SOC 2 compliance alone — without an independent SOC 2 examination — does not produce a report that can be shared with customers or used to satisfy vendor assurance requirements. The SOC 2 attestation report produced after a formal SOC 2 audit is the document that carries independent assurance value. Chicago organizations that have implemented controls internally but not yet undergone an independent SOC 2 examination cannot represent themselves as SOC 2 certified to customers or prospects.
Who Requires SOC 2 Certification in Chicago?
SOC 2 Certification is most commonly required by organizations that store, process, or transmit customer data on behalf of other businesses. In Chicago, this includes SaaS companies serving enterprise clients, cloud infrastructure providers, healthcare IT vendors processing protected health information, fintech companies managing financial transaction data, payment processors, managed security service providers, business process outsourcing firms, and insurance technology platforms. Enterprise procurement teams and vendor risk management programs routinely require SOC 2 attestation reports before onboarding new vendors or renewing existing contracts.
Chicago’s position as a major U.S. financial center means that financial services firms and their technology vendors face particularly strong demand for SOC 2 attestation. Institutions regulated by the Office of the Comptroller of the Currency, the Federal Reserve, and the Illinois Department of Financial and Professional Regulation increasingly require third-party service providers to furnish current SOC 2 Type 2 reports as part of third-party risk management programs. Similarly, healthcare organizations subject to HIPAA and health IT vendors serving Chicago’s extensive hospital network frequently require SOC 2 reports from their technology partners as a condition of onboarding.

ENQUIRE NOW
Related Resources
Related Services in Chicago
SOC 2 Type I vs. SOC 2 Type II: Explicit Comparison for Chicago Organizations
SOC 2 examinations are conducted as either Type 1 or Type 2 engagements, each serving a distinct purpose and providing a different level of assurance. Understanding the difference between SOC 2 Type 1 and Type 2 reports is essential for Chicago organizations determining which engagement structure aligns with their customer requirements, timeline, and risk profile. The selection between Type 1 and Type 2 directly affects the scope of the SOC 2 audit, the duration of fieldwork, and the nature of assurance the resulting report provides to recipients.
SOC 2 Type 1: Design Effectiveness at a Point in Time
A SOC 2 Type 1 report evaluates whether an organization’s controls are suitably designed to meet the selected Trust Services Criteria as of a specific date. The Type 1 examination does not assess whether controls have operated effectively over a period of time. Instead, the Licensed CPA Firm examines the organization’s system description, control documentation, and control design to determine whether the controls — if operating as described — would satisfy the applicable Trust Services Criteria. The resulting Type 1 attestation report reflects the state of controls at a single point in time.
For Chicago organizations new to the SOC 2 examination process, a Type 1 engagement can serve as a structured starting point. It establishes a documented control environment prior to the longer observation period required for a Type 2 report. However, many enterprise customers and regulated industry purchasers specifically require a SOC 2 Type 2 report and will not accept a Type 1 as a substitute. Chicago fintech companies and financial services technology vendors should confirm whether their target customers require Type 2 coverage before scoping their initial SOC 2 engagement.
SOC 2 Type 2: Operating Effectiveness Over a Review Period
A SOC 2 Type 2 report evaluates both the design and the operating effectiveness of controls over a defined observation period — typically spanning a minimum of six months, and commonly twelve months for established organizations pursuing annual reporting cycles. During the observation period, the Licensed CPA Firm collects and tests evidence of control operation across the entire review window. Control testing includes examination of logs, configuration records, access provisioning evidence, incident response documentation, change management records, vendor assessment evidence, and other artifacts demonstrating that controls functioned consistently throughout the period under review.
The SOC 2 Type 2 report is the primary attestation document demanded by enterprise customers, financial institutions, healthcare organizations, and regulated industry procurement programs. Its coverage of operating effectiveness over time provides substantially greater assurance than a Type 1 report, because it demonstrates that controls were not merely designed correctly but also executed consistently. Chicago SaaS companies, cloud service providers, managed service providers, and data processing organizations serving enterprise clients almost universally maintain annual SOC 2 Type 2 examination cycles to meet ongoing customer and contractual requirements.
Comparison of SOC 2 Type 1 and Type 2 Reports
| Characteristic | SOC 2 Type 1 | SOC 2 Type 2 |
|---|---|---|
| Assessment Focus | Control design evaluated at a single point in time | Control design and operating effectiveness evaluated over a defined period |
| Observation Period | None — single date assessment | Minimum 6 months; typically 12 months for annual cycles |
| Evidence Collected | Design documentation and written system description | Ongoing operational evidence collected across the full review period |
| Common Use Case | Initial SOC 2 engagement or control design baseline | Enterprise customer requirements and annual attestation cycles |
| Report Acceptance | Limited — many enterprise and regulated customers require Type 2 | Broadly accepted by enterprise, financial services, and healthcare buyers |
The Five AICPA Trust Services Criteria Explained
The five AICPA Trust Services Criteria categories define the specific domains evaluated during a SOC 2 examination. Each category contains criteria organized by topic, with associated points of focus describing relevant control attributes. An organization’s SOC 2 scope determines which categories are included. The Security category is mandatory for all SOC 2 engagements. The Availability, Processing Integrity, Confidentiality, and Privacy categories are included based on the organization’s service commitments, system characteristics, and the nature of customer data processed.
The Security category — formally designated as the Common Criteria (CC) — is the foundational and only mandatory Trust Services Criteria category in every SOC 2 examination. Security criteria address nine topic areas: control environment (CC1), communication and information (CC2), risk assessment (CC3), monitoring of controls (CC4), control activities (CC5), logical and physical access controls (CC6), system operations (CC7), change management (CC8), and risk mitigation (CC9). Each criterion within these areas specifies control attributes that auditors evaluate when assessing the organization’s overall security posture.
For Chicago technology companies and cloud service providers, the Security criteria encompass the full breadth of an organization’s information security program. Auditors evaluate logical access controls — including multi-factor authentication, role-based access provisioning, privileged access management, and access review processes. Physical security controls at data centers and office locations, network security configurations, endpoint protection, vulnerability management programs, security incident detection and response procedures, and encryption practices are all subject to examination under the Common Criteria. A SOC 2 audit firm in Chicago evaluating Security criteria will request evidence across all nine Common Criteria topic areas to determine whether controls are designed and operating effectively.
The Availability category addresses whether systems are available for operation and use as committed to customers. Availability criteria evaluate performance monitoring, capacity management, disaster recovery planning, backup procedures, and incident response capabilities that affect system uptime. Chicago cloud infrastructure providers, SaaS platforms with defined service level agreements, and managed service providers frequently include Availability in their SOC 2 scope because their customer commitments explicitly reference system uptime and recovery time objectives.
The Processing Integrity category addresses whether system processing is complete, valid, accurate, timely, and authorized. This category is most relevant to organizations that process financial transactions, execute computational workflows, or perform data transformation services on behalf of customers. Chicago fintech companies, payment processors, and financial data analytics firms often include Processing Integrity in their SOC 2 scope to address customer concerns about the accuracy and completeness of data processing activities.
The Confidentiality category evaluates controls over information designated as confidential — including encryption, access restrictions, and disposal procedures. The Privacy category, applicable when organizations collect or use personal information, evaluates controls across the full information lifecycle in alignment with the AICPA’s Generally Accepted Privacy Principles.
The selection of Trust Services Criteria categories for a SOC 2 examination is driven by the organization’s service commitments to customers, the nature of data processed, and contractual or regulatory requirements. During scope definition, the Licensed CPA Firm and the organization review system documentation, customer agreements, and data flow diagrams to determine which criteria categories are applicable. Including categories that do not reflect the organization’s actual system commitments or data handling practices can result in unnecessary examination scope and control testing without corresponding value to report recipients.
Chicago organizations across industries typically include at minimum Security and one or more additional categories. Healthcare IT vendors processing patient data commonly include Privacy alongside Security. Financial services technology firms frequently add Availability and Confidentiality. SaaS platforms with defined uptime commitments include Availability. Organizations providing data analytics or automated processing services often add Processing Integrity. The resulting SOC 2 scope reflects the specific risk profile and customer expectations of each organization — ensuring the attestation report addresses the areas of highest relevance to its recipients.
- ✓Security: The Common Criteria (Mandatory)
- ✓Availability, Processing Integrity, Confidentiality, and Privacy
- ✓Selecting Trust Services Criteria for a Chicago SOC 2 Engagement
SOC 2 Certification Audit Process in Chicago
The SOC 2 Certification audit process in Chicago follows a structured sequence of examination stages conducted by a Licensed CPA Firm under AICPA AT-C Section 205 attestation standards. Each stage is designed to evaluate specific aspects of the organization’s control environment, generate documented evidence, and support the auditor’s ultimate opinion on whether controls satisfy the applicable Trust Services Criteria. This process applies equally to organizations pursuing a first-time SOC 2 examination and those maintaining annual attestation cycles.
Scope definition is the initial and most consequential stage of the SOC 2 examination process. The Licensed CPA Firm works with the organization to identify the system under examination — including the infrastructure components, software applications, data flows, personnel, and procedures that constitute the in-scope system. System boundaries must be clearly defined to ensure the examination covers all components relevant to the services provided to customers. Incomplete scope definition can result in attestation reports that fail to address the controls customers and stakeholders consider most important.
During scope definition, the auditor and the organization determine which Trust Services Criteria categories apply, identify subservice organizations (third-party vendors whose services form part of the in-scope system), and establish the review period for Type 2 engagements. Chicago organizations commonly use cloud infrastructure providers such as AWS, Microsoft Azure, or Google Cloud as subservice organizations. The SOC 2 examination scope must address how subservice organization controls interact with the in-scope organization’s own controls to meet the applicable Trust Services Criteria.
The organization’s management prepares a written system description that forms the foundation of the SOC 2 attestation report. This description must accurately cover the services provided, the infrastructure and software components, the personnel and procedures involved, and the controls in place to meet the applicable Trust Services Criteria. The AICPA prescribes specific elements that must be addressed — including system boundaries, service commitments and system requirements, system components, and how the system addresses the applicable criteria.
The Licensed CPA Firm reviews the system description for completeness, accuracy, and consistency with the control environment observed during fieldwork. Discrepancies between the system description and actual control operation must be addressed before the attestation report can be finalized. For Chicago organizations undergoing their first SOC 2 audit, the system description preparation process frequently reveals gaps in control documentation and operational record-keeping that need to be resolved prior to completing the examination.
Evidence collection and audit fieldwork constitute the core examination phase of the SOC 2 audit process. The Licensed CPA Firm requests and reviews a defined set of evidence artifacts demonstrating control operation across the applicable Trust Services Criteria. Evidence types include system-generated logs, configuration exports, access provisioning and review records, incident tickets, change management approval records, vendor assessment documentation, policy and procedure documents, training completion records, and penetration testing reports. Each piece of evidence is evaluated against the specific control activity it is intended to support.
For SOC 2 Type 2 examinations, evidence must be drawn from across the full observation period to demonstrate consistent control operation. Auditors apply sampling techniques to select evidence populations representative of the review period. Control failures, evidence gaps, or inconsistencies identified during fieldwork are documented as exceptions or deviations. The nature, frequency, and impact of any control deviations affect the auditor’s evaluation of operating effectiveness and may result in qualified opinions or findings noted in the attestation report. Chicago organizations with centralized logging systems, automated monitoring tools, and documented change management workflows are better positioned to produce complete, timely evidence during this phase of the SOC 2 audit.
Following evidence collection and control testing, the Licensed CPA Firm conducts a formal review of identified exceptions, deviations, and nonconformities. Each issue is evaluated to determine its significance, its impact on the overall control environment, and whether it affects the auditor’s opinion on control design or operating effectiveness. Management is provided an opportunity to respond to identified findings, and those responses may be included in the SOC 2 attestation report.
The SOC 2 attestation report is finalized and issued upon completion of the nonconformity review and quality control procedures required under AICPA standards. The report includes the independent auditor’s opinion, the organization’s system description, a description of the applicable Trust Services Criteria, the controls identified by management, the auditor’s testing procedures and results, and any identified exceptions. The completed report is issued to the organization’s management and distributed to report recipients in accordance with the organization’s distribution policy. SOC 2 reports are generally treated as confidential documents and shared under non-disclosure agreements with current and prospective customers and business partners.
- Scope Definition: Identify system boundaries, applicable Trust Services Criteria categories, and in-scope infrastructure, software, personnel, and procedures.
- Audit Program Determination: Establish the examination approach, evidence requirements, sampling methodology, and control testing procedures based on the selected criteria and engagement type.
- System Description Review: Evaluate management’s written system description for accuracy, completeness, and consistency with the defined control environment.
- Stage 1 Assessment (Type 1): Evaluate control design effectiveness as of the specified report date against applicable Trust Services Criteria.
- Observation Period Monitoring (Type 2): Collect and evaluate evidence of control operation across the defined review period — minimum six months.
- Control Testing and Evidence Evaluation: Apply substantive testing, inspection, inquiry, and observation procedures to evaluate evidence produced by the organization.
- Nonconformity Identification and Review: Document control deviations and exceptions, evaluate their significance, and obtain management responses.
- Attestation Report Drafting: Prepare the formal SOC 2 attestation report including auditor opinion, system description, control descriptions, testing results, and exceptions.
- Quality Control Review: Complete firm-level quality control procedures required under AICPA standards prior to report issuance.
- Report Issuance: Issue the completed SOC 2 attestation report to the organization and applicable report recipients.
- ✓Stage 1: Scope Definition and System Boundary Determination
- ✓Stage 2: System Description Preparation and Review
- ✓Stage 3: Evidence Collection and Audit Fieldwork
- ✓Stage 4: Nonconformity Review and Report Issuance
- ✓SOC 2 Audit Process: Sequential Steps
SOC 2 Compliance Requirements for Chicago Businesses
SOC 2 compliance requirements for Chicago businesses encompass the internal controls, policies, procedures, and operational practices that align with the applicable Trust Services Criteria. While SOC 2 compliance alone does not produce an attestation report, it represents the control environment that a Licensed CPA Firm evaluates during the SOC 2 examination. Organizations must demonstrate that their control environment is both designed appropriately and functioning consistently before a clean SOC 2 attestation can be issued.
Documentation is a foundational requirement for SOC 2 compliance and examination. Organizations must maintain formal, written documentation of their information security policies, access control procedures, change management workflows, incident response plans, business continuity and disaster recovery plans, vendor management procedures, and risk assessment processes. Policy documents must be current, approved by management, and communicated to relevant personnel. Procedures must describe the specific steps followed to implement each policy and must align with the actual operational practices observed during the SOC 2 audit.
Chicago organizations across technology, financial services, healthcare IT, and professional services industries frequently cite documentation completeness as the primary control environment challenge identified during a first SOC 2 examination. Auditors evaluate not only whether policies exist, but whether they are implemented as written and whether evidence of policy adherence is systematically retained. Organizations that maintain audit trails, change tickets, access review records, and incident logs in structured systems are significantly better positioned to produce complete evidence during SOC 2 audit fieldwork.
Technical controls evaluated during a SOC 2 examination span the full technology stack of the in-scope system. Logical access controls must implement the principle of least privilege, require multi-factor authentication for privileged and remote access, enforce role-based access provisioning, and include periodic access reviews that identify and remove inappropriate access rights. Network security controls must include firewalls, intrusion detection capabilities, network segmentation, and encrypted communications. Endpoint protection controls must address malware prevention, patch management, and device configuration standards.
Encryption requirements under the SOC 2 examination framework address both data in transit and data at rest. Organizations must demonstrate that sensitive customer data is encrypted using industry-standard algorithms and sound key management practices. Vulnerability management programs must include regular scanning of infrastructure components and timely remediation of identified vulnerabilities based on defined severity thresholds. Logging and monitoring controls must capture security-relevant events, generate alerts for anomalous activity, and retain logs for a defined period sufficient to support incident investigation and SOC 2 audit evidence requirements.
Operational requirements for SOC 2 compliance address the people and process dimensions of the control environment. Organizations must conduct background checks on personnel with access to in-scope systems and customer data. Security awareness training must be provided to all relevant personnel on a defined schedule, with completion tracked and documented. Performance review and disciplinary procedures must address security policy violations. Organizational structures must define clear accountability for security control ownership and operation.
Vendor management requirements address the risk posed by third-party service providers whose services affect the in-scope system. Organizations must maintain an inventory of third-party vendors with access to in-scope systems or customer data, conduct periodic risk assessments of significant vendors, and review vendor SOC 2 reports or other security attestations to evaluate third-party control environments. Change management controls must ensure that system changes — including software deployments, infrastructure modifications, and configuration updates — are authorized, tested, and approved prior to implementation in production environments.
- ✓Formal information security policy documented, approved, and communicated to all relevant personnel
- ✓Logical access controls implementing least privilege, MFA, and periodic access reviews
- ✓Encryption of sensitive data in transit and at rest using industry-standard algorithms
- ✓Vulnerability management program with defined scanning cadence and remediation timelines
- ✓Centralized logging and monitoring with alerting for security-relevant events
- ✓Incident response plan with defined response procedures, escalation paths, and post-incident review
- ✓Change management process requiring authorization, testing, and approval for all production changes
- ✓Business continuity and disaster recovery plans with defined RTO and RPO objectives, tested periodically
- ✓Third-party vendor risk management program with vendor inventory and periodic risk assessments
- ✓Security awareness training for all personnel with access to in-scope systems, documented on an annual basis
- ✓Documentation Requirements
- ✓Technical Control Requirements
- ✓Operational and Organizational Requirements
- ✓SOC 2 Compliance Requirements Summary
Industry-Specific SOC 2 Demand in Chicago
Chicago’s diverse economy generates SOC 2 demand across multiple industry sectors, each with distinct drivers and customer expectations. The city’s concentration of enterprise technology firms, financial institutions, healthcare organizations, insurance companies, logistics businesses, and professional services providers creates a layered ecosystem where SOC 2 attestation reports circulate as standard vendor assurance documents. Understanding the industry-specific context for SOC 2 Certification in Chicago enables organizations to scope their examinations appropriately and address the specific control expectations of their customer base.
Financial Services and Fintech
Chicago is one of the foremost financial centers in the United States, home to the Chicago Mercantile Exchange, the Chicago Board Options Exchange, major commercial banks, insurance conglomerates, asset management firms, and a rapidly expanding fintech sector. SOC 2 Certification for Chicago fintech companies and financial services technology vendors is driven by both customer demand and regulatory expectation. Financial institutions subject to GLBA, OCC guidance, and Federal Reserve supervisory expectations for third-party risk management require technology vendors to provide current SOC 2 Type 2 reports as part of annual vendor review cycles.
Chicago fintech companies providing payment processing, trading technology, wealth management platforms, lending platforms, and financial data analytics services routinely maintain SOC 2 Type 2 attestations covering Security, Availability, Confidentiality, and Processing Integrity. The Processing Integrity criteria category is particularly relevant to organizations whose services involve financial transaction processing, where accuracy, completeness, and timeliness of processing are contractual commitments subject to customer scrutiny. SOC 2 Certification for Chicago financial services organizations therefore typically encompasses a broader set of Trust Services Criteria than organizations in other industries.
Healthcare Technology and Health IT
Chicago’s healthcare technology sector includes electronic health record vendors, health information exchange platforms, medical device connectivity solutions, revenue cycle management companies, telehealth providers, and clinical decision support software firms. These organizations process protected health information subject to HIPAA requirements and serve hospital networks, physician practices, and health systems that require independent verification of security and privacy controls before onboarding technology partners. SOC 2 compliance that Chicago healthcare IT vendors demonstrate through Type 2 attestation is frequently paired with HIPAA Business Associate Agreement requirements.
Healthcare IT organizations in Chicago typically include the Privacy criteria category in their SOC 2 scope — in addition to Security and Availability — reflecting the sensitivity of patient data and the regulatory expectations of their hospital and health system customers. The Privacy criteria evaluate controls across the full personal information lifecycle, from collection through disposal, and address practices related to notice, choice and consent, access, disclosure, and data integrity. SOC 2 attestation covering Privacy is increasingly recognized as a complement to HIPAA compliance documentation for health IT vendors seeking to address the full range of healthcare customer assurance requirements.
SaaS, Cloud, and Technology Companies
Chicago’s technology sector encompasses hundreds of SaaS companies, cloud infrastructure providers, software development firms, managed service providers, cybersecurity firms, AI and machine learning companies, and enterprise software vendors. The SOC 2 audit that Chicago technology companies most commonly undergo is a Type 2 examination covering Security and Availability — reflecting the centrality of system security and uptime to customer expectations in the SaaS and cloud markets. Enterprise procurement programs at Chicago’s largest corporations routinely require current SOC 2 Type 2 reports from SaaS vendors before approving software deployments that involve customer or employee data.
Managed service providers and managed security service providers operating in Chicago serve both local and national client bases that demand independent verification of the security controls protecting their managed environments. These organizations frequently include Security, Availability, and Confidentiality in their SOC 2 scope, as customers entrust them with access to sensitive IT environments, confidential business data, and security event information. Annual SOC 2 Type 2 examination cycles are standard practice for established managed service providers maintaining multiple enterprise customer relationships.
Logistics, Insurance, and Professional Services
Chicago’s position as a major logistics hub — combined with its concentration of insurance companies and professional services firms — creates additional SOC 2 demand from sectors that handle sensitive supply chain data, policyholder information, and client confidential information. Logistics technology providers serving major retailers and manufacturers process shipment data, inventory information, and supply chain analytics that enterprise customers treat as confidential business information. SOC 2 examinations covering Confidentiality and Security are increasingly required by these enterprise logistics customers as part of their third-party risk programs.
Insurance technology companies in Chicago — including InsurTech startups and established insurance software providers — process policyholder personal information and underwriting data requiring rigorous privacy and confidentiality controls. SOC 2 attestation reports covering Privacy and Confidentiality are frequently required by insurance carrier partners and reinsurance organizations as a condition of data sharing arrangements. Professional services firms providing legal technology, accounting software, and HR management systems also face growing SOC 2 requirements from enterprise clients who treat client data processed through these platforms as subject to their own vendor risk management obligations.
SOC 2 Attestation Chicago: Evidence Collection and Audit Fieldwork
The SOC 2 attestation Chicago organizations receive is grounded in the evidence collection and fieldwork activities conducted by the Licensed CPA Firm during the examination. The quality, completeness, and organization of evidence produced by the organization directly affect the efficiency of the SOC 2 audit process and the findings documented in the attestation report. Understanding the evidence requirements for a SOC 2 examination enables Chicago organizations to structure their control environments and record-keeping practices in ways that support systematic evidence production during fieldwork.
Categories of SOC 2 Audit Evidence
SOC 2 audit evidence falls into several categories based on the control activities being tested. System-generated evidence includes log exports from identity and access management systems, SIEM platforms, change management tools, vulnerability scanners, backup systems, and monitoring dashboards. Configuration evidence includes exported system configurations for firewalls, cloud environments, endpoint management platforms, and database access controls. Process evidence includes completed change management tickets, access review records, incident response documentation, vendor assessment reports, and security awareness training completion records.
Personnel-based evidence includes background check records, security training acknowledgments, employment agreements containing confidentiality provisions, and organizational charts demonstrating accountability structures. Third-party evidence includes vendor SOC 2 reports, penetration testing reports from qualified third parties, and certificates of insurance. For SOC 2 Type 2 examinations, evidence must be available for the entire observation period — meaning organizations must retain logs, tickets, and records in systems that support retrieval of historical data across the full review window. Chicago organizations using cloud-based ticketing, identity management, and logging systems with configurable retention policies are generally well-positioned to meet this requirement.
Auditor Testing Procedures During Fieldwork
Auditors conducting a SOC 2 examination apply four primary testing procedures: inquiry, observation, inspection, and re-performance. Inquiry involves interviewing personnel responsible for control operation to understand how controls function in practice. Observation involves the auditor directly viewing a control activity being performed — such as a data center access control procedure or a change management approval workflow. Inspection involves reviewing documentation, system outputs, and physical or logical artifacts to verify that control activities occurred as described. Re-performance involves the auditor independently executing a procedure to verify it produces the expected result.
For each control activity tested, auditors document the testing procedure applied, the evidence examined, the population sampled, and the results observed. Deviations from expected control operation are documented as exceptions and evaluated for their impact on the overall control conclusion. The SOC 2 examination that Chicago organizations undergo is an independent, evidence-based process that does not rely on management representations alone. The auditor’s opinion in the attestation report reflects the totality of evidence gathered and the significance of any identified control deviations relative to the applicable Trust Services Criteria.
Centralized Logging and Monitoring as SOC 2 Evidence Infrastructure
Centralized logging and monitoring systems serve as critical evidence infrastructure for SOC 2 Type 2 examinations. These systems collect security-relevant events from across the organization’s technology stack — including authentication events, privileged access activities, configuration changes, network traffic anomalies, and application errors — and store them in a single, queryable location. During a SOC 2 audit, auditors request log data to verify that monitoring controls are operational, that alerts are generated for defined event types, and that security events are investigated and resolved within defined timeframes.
Organizations that implement Security Information and Event Management (SIEM) platforms or equivalent centralized log management solutions are better positioned to produce audit-ready evidence during SOC 2 fieldwork. Log data must be protected against unauthorized modification to ensure its integrity as audit evidence. Log retention policies must align with the SOC 2 review period — typically requiring at minimum twelve months of log retention for organizations maintaining annual Type 2 examination cycles. Chicago technology organizations building or evaluating their logging and monitoring infrastructure should treat SOC 2 evidence requirements as a design consideration, not a retrospective compliance activity.
Benefits of SOC 2 Certification for Chicago Organizations
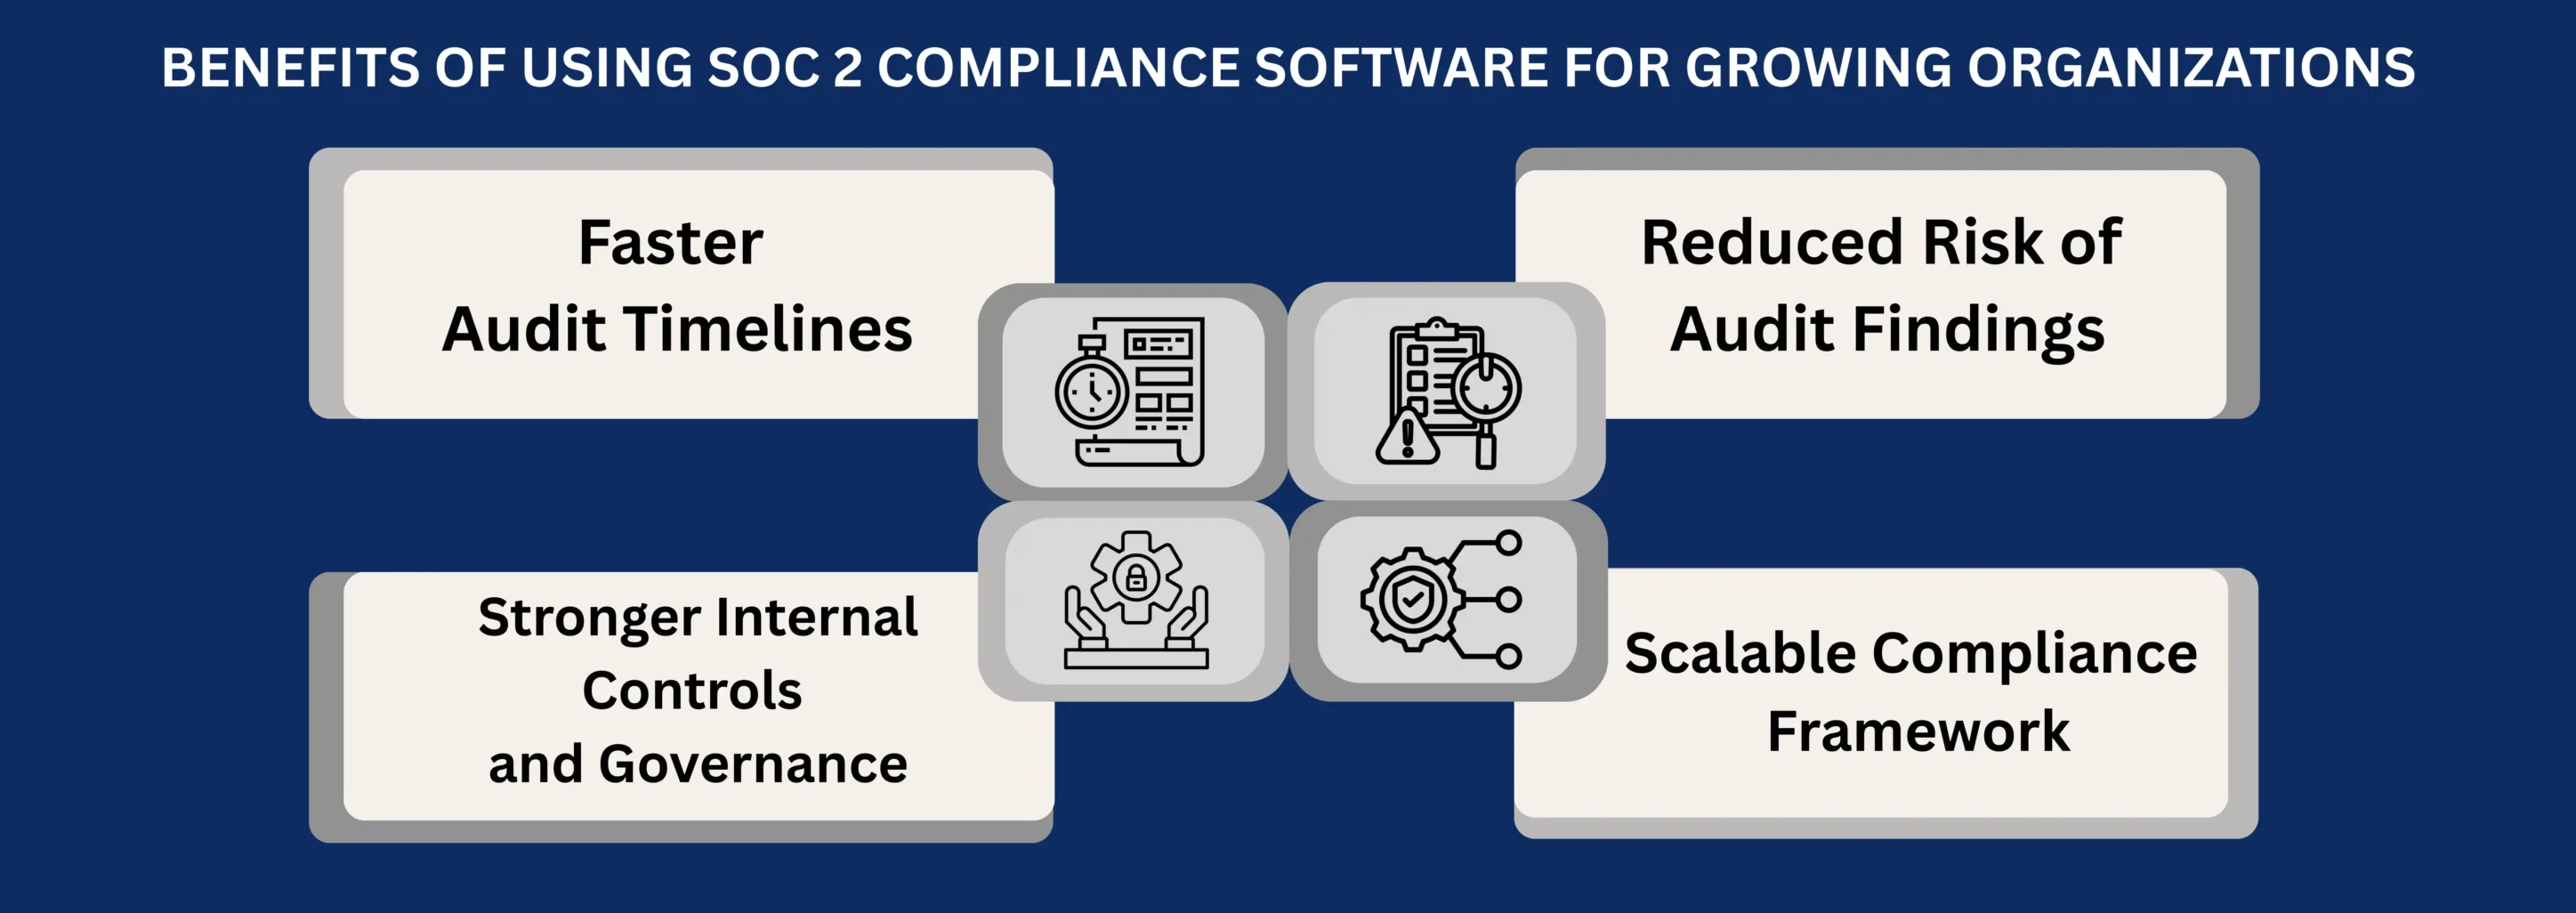
SOC 2 Certification in Chicago delivers measurable business benefits to organizations across technology, financial services, healthcare IT, logistics, insurance, and professional services sectors. The value of SOC 2 attestation extends well beyond regulatory compliance — encompassing competitive differentiation, customer trust, operational discipline, and risk reduction. Chicago organizations that maintain current SOC 2 Type 2 attestations are positioned to address customer due diligence requirements efficiently and demonstrate a documented commitment to information security through independent, third-party verification.
A current SOC 2 Type 2 attestation report enables Chicago organizations to satisfy enterprise customer security due diligence requirements without lengthy custom security questionnaire processes. Enterprise procurement teams, vendor risk management programs, and information security departments increasingly accept SOC 2 reports as primary evidence of vendor security posture. Organizations that can produce a current SOC 2 Type 2 report during the sales process demonstrate operational maturity, reduce the friction associated with security reviews, and accelerate deal velocity — enabling access to enterprise customer segments that would otherwise be inaccessible without independent attestation.
SOC 2 attestation also supports contract renewal processes with existing customers. Many enterprise customers require annual SOC 2 Type 2 reports from current vendors as a condition of contract renewal under their third-party risk management programs. Organizations that maintain continuous SOC 2 examination cycles — where each year’s Type 2 report covers the period immediately following the prior year’s report — are able to provide customers with uninterrupted attestation coverage and avoid contract disruption caused by lapsed reports.
The SOC 2 examination process itself produces operational benefits by identifying control gaps, inconsistencies in policy adherence, and documentation deficiencies that may not be visible to internal management without an independent review. Organizations that complete annual SOC 2 Type 2 examinations consistently report improvements in access management practices, change management discipline, incident response documentation, and vendor oversight procedures as a direct result of the examination cycle. These improvements reduce the probability and potential impact of security incidents by strengthening the control environment against which threats and vulnerabilities are managed.
Risk reduction is a quantifiable benefit of sustained SOC 2 compliance for Chicago organizations. A well-designed and consistently operated control environment that satisfies the Trust Services Criteria reduces the likelihood of unauthorized access incidents, data breaches, processing errors, and system availability failures. The financial and reputational consequences of security incidents are substantially higher for organizations that process customer data on behalf of enterprises — making the investment in SOC 2 compliance and independent attestation directly relevant to enterprise risk management objectives.
- ✓Independent third-party verification of security controls satisfies enterprise customer due diligence requirements
- ✓SOC 2 Type 2 reports accepted by vendor risk management programs in financial services, healthcare, and enterprise technology sectors
- ✓Accelerated enterprise sales cycles by addressing security questionnaire requirements with a formal SOC 2 attestation report
- ✓Annual examination cycles maintain continuous attestation coverage for ongoing customer contract renewal requirements
- ✓Identification of control gaps and operational inconsistencies through independent examination strengthens the internal control environment
- ✓Documented control framework reduces the probability and impact of security incidents, data breaches, and availability failures
- ✓Competitive differentiation in Chicago’s technology and financial services markets where SOC 2 Certification is a baseline customer expectation
- ✓Supports compliance with HIPAA, GLBA, and other regulatory frameworks through aligned control structure and independent verification
- ✓Facilitates access to regulated industry customers — financial institutions, healthcare organizations, insurers — that require vendor SOC 2 attestation
- ✓Demonstrates organizational commitment to data security and privacy to customers, partners, and prospective employees
- ✓Customer Trust and Enterprise Sales Enablement
- ✓Operational Control Improvement and Risk Reduction
- ✓Benefits of SOC 2 Certification: Summary
SOC 2 Certification Cost and Timeline in Chicago
The timeline for completing a SOC 2 examination in Chicago varies based on the engagement type, the scope of Trust Services Criteria included, the size and complexity of the organization, and the maturity of the existing control environment. Understanding the typical duration of each examination phase enables Chicago organizations to plan their SOC 2 audit schedule in alignment with customer commitments, contract deadlines, and business development objectives. SOC 2 examinations are structured engagements with defined phases, and the total duration from scope agreement to report issuance depends on the efficiency of evidence production and the completeness of the organization’s control documentation.
SOC 2 Type 1 Timeline
A SOC 2 Type 1 examination typically requires four to eight weeks from the initiation of fieldwork to the issuance of the attestation report. The Type 1 timeline includes scope definition, system description review, control design evaluation, evidence collection, nonconformity review, and report drafting. Because Type 1 examinations do not require an observation period, the total engagement duration is significantly shorter than a Type 2 examination. Organizations with well-documented control environments and complete policy documentation can often complete a Type 1 examination at the shorter end of this range. Organizations with documentation gaps or complex system environments may require additional time.
SOC 2 Type 2 Timeline
A SOC 2 Type 2 examination has a total duration that includes both the observation period and the post-period fieldwork and reporting phases. The observation period for a first-time Type 2 engagement is typically six months, though some organizations elect a three-month initial period when specifically agreed with their Licensed CPA Firm. Following the close of the observation period, fieldwork, evidence review, and report drafting typically require an additional six to ten weeks. Organizations pursuing a twelve-month observation period should plan for a total engagement duration of approximately fourteen to fifteen months from the start of the observation period to report issuance.
Chicago organizations that must produce a current SOC 2 Type 2 report to meet a specific customer contract deadline or enterprise sales requirement should initiate the SOC 2 examination process well in advance of the target report date. The observation period must conclude before fieldwork begins, and fieldwork must be completed before the report can be issued. Organizations planning annual SOC 2 examination cycles typically structure their Type 2 periods to produce a new report each year — with the current year’s observation period beginning immediately after the prior year’s period ends — to maintain continuous attestation coverage.
Factors Affecting SOC 2 Examination Duration
| Factor | Impact on Timeline |
|---|---|
| Number of Trust Services Criteria categories in scope | Additional categories increase evidence requirements and extend overall testing duration |
| Organization size and system complexity | Larger organizations with complex technology stacks require more extensive evidence collection and longer fieldwork |
| Control documentation completeness | Incomplete documentation at examination initiation extends fieldwork and may delay report issuance |
| Evidence organization and retrieval efficiency | Organizations with structured evidence management systems produce evidence faster, reducing total fieldwork duration |
| Observation period length (Type 2 only) | Longer observation periods increase evidence volume but do not necessarily extend the post-period fieldwork phase |
Why CertPro — A Licensed CPA Firm — Conducts SOC 2 Audits in Chicago
CertPro is a Licensed CPA Firm authorized to conduct SOC 2 examinations under AICPA AT-C Section 205 attestation standards. Only a Licensed CPA Firm holding the appropriate credentials, independence qualifications, and professional competency can issue a valid SOC 2 attestation report. Organizations in Chicago and across Illinois that receive SOC 2 examination reports from entities other than a Licensed CPA Firm have not received a valid SOC 2 attestation and cannot represent themselves as SOC 2 certified to customers or regulatory stakeholders.
Independence and AICPA Professional Standards
AICPA attestation standards require that the CPA firm conducting a SOC 2 examination maintain independence from the organization under examination. Independence requirements prohibit the examining firm from holding financial interests in the subject organization, providing certain non-attest services that could compromise objectivity, or having personnel relationships with client management that could impair judgment. These independence requirements are foundational to the credibility of the SOC 2 attestation report, as report recipients rely on the assumption that the auditor has evaluated controls objectively and without influence from the organization’s management.
CertPro maintains strict independence from all organizations for which it conducts SOC 2 examinations, in full compliance with AICPA independence requirements. This independence is preserved throughout the engagement — from scope definition through report issuance. CertPro does not provide consulting, implementation, policy development, control design, or remediation services to organizations for which it conducts SOC 2 examinations. This ensures that each examination reflects an objective third-party assessment of the organization’s actual control environment, rather than controls designed or implemented by the examining firm.
Examination Methodology and Sector Experience
CertPro’s SOC 2 examination methodology is structured around the AICPA’s Trust Services Criteria and AT-C Section 205 requirements. The examination approach encompasses structured scope definition, system description review, evidence program design, control testing, exception evaluation, and formal report production. CertPro conducts SOC 2 examinations for organizations across Chicago’s technology, financial services, healthcare IT, logistics technology, insurance, and professional services sectors — applying examination procedures calibrated to the specific control environment and system characteristics of each organization under review.
As a SOC 2 audit firm in Chicago, CertPro understands the industry-specific control expectations and customer requirements that drive SOC 2 demand across the Chicago market. The SOC 2 examination Chicago clients receive is conducted by CPA-credentialed professionals with expertise in information technology controls, cloud architecture security, financial services compliance requirements, healthcare privacy standards, and the operational control environments typical of organizations serving enterprise customers. The resulting SOC 2 attestation reports meet the standards required by enterprise customer vendor risk management programs and satisfy the due diligence requirements of regulated industry purchasers.
Report Validity and Annual Examination Cycles
SOC 2 attestation reports do not carry an indefinite validity period. A SOC 2 Type 2 report covers a specific observation period and is considered current for the twelve months following the end of that period — though customer expectations and industry practice often demand a report issued within the prior six to twelve months. Organizations that allow their SOC 2 attestation to lapse risk losing access to customer procurement programs that require current attestation as a condition of vendor approval. Annual SOC 2 Type 2 examination cycles — where each year’s observation period begins immediately after the prior year’s period concludes — maintain continuous attestation coverage and ensure the organization can produce a current report at any point during the year.
SOC 2 Certification in Chicago: Requirements Summary
The requirements for SOC 2 Certification in Chicago are defined by the AICPA Trust Services Criteria and the AT-C Section 205 attestation standards under which examinations are conducted. Meeting these requirements involves establishing a documented control environment, maintaining operational records sufficient to demonstrate control operation over time, and engaging a Licensed CPA Firm to conduct an independent examination. The following summary identifies the primary requirements Chicago organizations must satisfy to achieve and maintain SOC 2 attestation.
| Requirement Category | Key Elements | Applicable Criteria |
|---|---|---|
| Access Control | MFA enforcement, least privilege principles, periodic access reviews, privileged access management | CC6 |
| Risk Management | Formal risk assessment process, maintained risk register, documented risk treatment decisions | CC3, CC9 |
| Change Management | Change authorization, pre-deployment testing, management approval, and controlled deployment procedures | CC8 |
| Incident Response | Incident detection capabilities, documented response procedures, escalation paths, and post-incident review process | CC7 |
| Vendor Management | Maintained vendor inventory, periodic third-party risk assessments, review of vendor SOC 2 or equivalent attestations | CC9 |
SOC 2 Certification in Chicago requires that organizations demonstrate consistent, documented control operation across the applicable Trust Services Criteria throughout the observation period. Organizations must retain evidence of control activities in retrievable form for the duration of the review period and beyond to support audit evidence requests. The organization’s management must formally attest to the accuracy of the system description included in the SOC 2 attestation report. Ongoing maintenance of SOC 2 Certification requires annual examination cycles conducted by a Licensed CPA Firm to produce current attestation reports acceptable to customers and business partners.
SOC 2 compliance refers to an organization’s internal adherence to policies and controls aligned with the Trust Services Criteria, without independent verification. SOC 2 Certification — technically called SOC 2 attestation — is issued by a Licensed CPA Firm following an independent examination. Only a formal SOC 2 attestation report produced by a Licensed CPA Firm constitutes verified, shareable assurance. Organizations cannot represent themselves as SOC 2 certified based on internal compliance efforts alone.
A SOC 2 Type 2 examination includes an observation period of at least six months, followed by a post-period fieldwork and reporting phase of six to ten weeks. First-time Type 2 engagements with a six-month observation period typically produce an attestation report within eight to nine months from examination initiation. Organizations pursuing a twelve-month observation period should plan for approximately fourteen to fifteen months total — from the start of the period to report issuance. The timeline depends on organization size, scope complexity, and evidence availability.
The Security category — also called the Common Criteria — is the only mandatory Trust Services Criteria category for every SOC 2 examination. The Availability, Processing Integrity, Confidentiality, and Privacy categories are optional and are included based on the organization’s service commitments, system characteristics, and customer contractual requirements. Chicago organizations in financial services, healthcare IT, and SaaS commonly include Availability and Confidentiality alongside Security, while healthcare IT vendors often add Privacy to address patient data protection requirements.
No. Only a Licensed CPA Firm holding the required credentials and independence qualifications under AICPA standards can conduct a SOC 2 examination and issue a valid SOC 2 attestation report. Consulting firms, cybersecurity companies, technology vendors, and advisory organizations cannot issue SOC 2 reports — regardless of the preparation services they provide. Documents labeled as SOC 2 reports issued by entities other than a Licensed CPA Firm are not valid SOC 2 attestations and will not be accepted by enterprise customers or regulated industry procurement programs.
A SOC 2 attestation report covers a defined observation period and is generally considered current for twelve months following the end of that period. However, many enterprise customers and regulated industry buyers expect a report issued within the prior six to twelve months. Organizations must complete annual SOC 2 examination cycles to maintain continuous attestation coverage. Allowing a SOC 2 report to lapse can disrupt vendor approval status with enterprise customers whose programs require a current attestation as a contract condition.
SOC 2 Certification in Chicago is most commonly required by organizations that store, process, or transmit customer data on behalf of other businesses. This includes SaaS companies, cloud service providers, managed service providers, fintech firms, healthcare IT vendors, payment processors, insurance technology companies, logistics technology providers, and business process outsourcing firms. Enterprise customers in financial services, healthcare, and technology sectors routinely require current SOC 2 Type 2 reports as a condition of vendor onboarding and contract renewal under third-party risk management programs.
The terms SOC 2 examination and SOC 2 audit are used interchangeably in practice. Technically, the AICPA standards use the term examination to describe the engagement conducted by a Licensed CPA Firm under AT-C Section 205. The term SOC 2 audit is more commonly used in commercial and marketing contexts. Both terms refer to the same independent, evidence-based process conducted by a Licensed CPA Firm to evaluate an organization’s controls against the applicable Trust Services Criteria and issue a formal SOC 2 attestation report.
The choice between SOC 2 and ISO 27001 depends primarily on the organization’s customer requirements and target markets. SOC 2 Certification in Chicago is most relevant for organizations serving U.S. enterprise customers — particularly in financial services, healthcare, SaaS, and technology sectors — where SOC 2 attestation is the dominant vendor assurance standard. ISO 27001 offers broader global recognition and is preferred in European and international markets. Organizations with both U.S. and international customer bases may ultimately pursue both certifications, with SOC 2 typically prioritized first for U.S.-focused organizations due to direct customer contract requirements.
A SOC 2 attestation report includes five primary sections: the independent service auditor’s report containing the auditor’s opinion; management’s description of the system; management’s assertion regarding the system description and control effectiveness; the applicable Trust Services Criteria; and the auditor’s description of tests of controls and results. For Type 2 reports, the testing section includes the specific procedures applied, the evidence examined, the population sampled, and the results observed for each control activity tested — including any identified exceptions or deviations from expected control operation.
- ✓Frequently Asked Questions: SOC 2 Certification in Chicago
- ✓What is the difference between SOC 2 certified and SOC 2 compliant?
- ✓How long does a SOC 2 Type 2 examination take for a Chicago organization?
- ✓Which Trust Services Criteria categories are mandatory for SOC 2 Certification in Chicago?
- ✓Can a consulting firm issue a SOC 2 attestation report?
- ✓How long is a SOC 2 attestation report valid?
- ✓What types of Chicago organizations most commonly require SOC 2 Certification?
- ✓What is the difference between a SOC 2 examination and a SOC 2 audit?
- ✓Should a Chicago organization pursue SOC 2 or ISO 27001 first?
- ✓What is included in a SOC 2 attestation report?
FAQ
▶
What is SOC 2 certification?
▶
What is the difference between SOC 2 certified and SOC 2 compliant?
▶
How long does a SOC 2 Type 2 examination take for a Chicago organization?
▶
Which Trust Services Criteria categories are mandatory for SOC 2 Certification in Chicago?
▶
Can a consulting firm issue a SOC 2 attestation report?
▶
How long is a SOC 2 attestation report valid?
▶
What types of Chicago organizations most commonly require SOC 2 Certification?
▶
What is the difference between a SOC 2 examination and a SOC 2 audit?
SOC 1 VS SOC 2: WHICH REPORT YOUR CUSTOMERS ACTUALLY ASK FOR
If you sell SaaS or provide outsourced services, you have likely been asked for a SOC report. However, the follow-up question is rarely easy to answer…
AICPA Issues New Guidance for Peer Reviewers Evaluating SOC 2 Engagements
AICPA SOC 2 guidance has been issued to help peer reviewers identify quality risks associated with SOC 2 engagements as the use of compliance automati…
SOC 2 Certified: What Does It Mean for Your Business
For companies that handle sensitive data or run cloud-based services, the question “Can you provide your SOC 2 report?” carries enormous weight. Yet, …
Get In Touch
have a question? let us get back to you.