
ISO 27001 Certification in Denmark
The ISO 27001 certification audit process follows a defined sequence of stages — from initial application through certification issuance and ongoing surveillance. CertPro CPA LLC conducts ISO 27001 certification audits for Denmark-based organizations in accordance with ISO/IEC 17021-1 and ISO/IEC 27006 requirements, which govern competence, consistency, and impartiality in management system certification. Each stage of the ISO 27001 audit is evaluation-focused and evidence-based, with findings documented in formal audit reports that form the basis of the certification decision.
OUR CLIENTS
What Is ISO 27001 Certification and Why Does It Matter for Danish Organizations?
ISO 27001 Certification in Denmark is formal third-party attestation issued by an accredited certification body confirming that an organization’s Information Security Management System (ISMS) conforms to the requirements of ISO/IEC 27001:2022. The standard provides a systematic framework for establishing, implementing, maintaining, and continually improving an ISMS — covering people, processes, and technology across the full scope of an organization’s information assets. Certification is awarded only after a structured ISO 27001 certification audit conducted by a qualified, independent auditor who evaluates documented evidence, operational controls, risk treatment decisions, and management system effectiveness against each clause of the standard.
For organizations operating in Denmark, ISO 27001 Certification carries particular commercial and regulatory significance. Denmark’s digital economy is one of the most advanced in Europe, with a dense concentration of SaaS providers, fintech firms, cloud infrastructure operators, pharmaceutical companies, healthcare entities, telecommunications providers, gaming companies, data centers, AI businesses, and e-commerce enterprises across Copenhagen, Aarhus, Odense, Aalborg, and the broader Danish technology corridor. These organizations routinely handle sensitive personal data, financial records, intellectual property, and critical operational systems — creating a high baseline expectation for structured information security governance from customers, regulators, and business partners alike.
ISO 27001 compliance in Denmark is increasingly referenced in vendor qualification processes, public-sector procurement frameworks, and cross-border commercial contracts. Danish organizations supplying services to EU institutions, multinational enterprises, financial sector clients, and healthcare systems are regularly required to demonstrate independently verified information security controls. ISO 27001 Certification provides that verification in a format recognized across the European Union and in major international markets including the United States, the United Kingdom, and Southeast Asia. The certification mark signals that an organization’s ISMS has been audited against a globally accepted standard — not merely self-assessed.
ISO/IEC 27001:2022 introduced important structural and control-level updates compared to the previous 2013 edition. The 2022 standard reorganized Annex A from 114 controls across 14 domains into 93 controls across four themes: Organizational, People, Physical, and Technological. Eleven new controls were introduced, addressing areas such as threat intelligence, cloud service security, data masking, information deletion, and physical security monitoring. Organizations certified under the 2013 edition were required to transition to ISO/IEC 27001:2022 by 31 October 2025 — a deadline set by accredited certification bodies internationally. Danish organizations initiating ISO 27001 certification after this date must demonstrate full conformance with the 2022 version of the standard.
ISMS certification under ISO 27001 also gives Danish organizations a structured framework for demonstrating accountability under the EU General Data Protection Regulation (GDPR) and the Danish Data Protection Act (Databeskyttelsesloven). While ISO 27001 Certification does not constitute legal compliance with GDPR or any other regulation, the documented risk assessment, control mapping, and management review processes embedded within an ISO 27001 ISMS directly support the technical and organizational measures that data protection law requires. Similarly, organizations subject to the NIS2 Directive or the Digital Operational Resilience Act (DORA) can use ISO 27001 audit evidence to substantiate cybersecurity and operational resilience controls to regulators. CertPro CPA LLC, a Licensed CPA Firm, conducts independent ISO 27001 certification audits for organizations across Denmark, issuing certification based on structured evidence evaluation and audit findings.

ENQUIRE NOW
Related Resources
Related Services in Denmark
ISO 27001 Certification Requirements for Danish Organizations
Achieving ISO 27001 Certification in Denmark requires an organization to demonstrate conformance with all mandatory clauses of ISO/IEC 27001:2022 — specifically Clauses 4 through 10 — and to implement controls from Annex A that are applicable based on its documented risk assessment and risk treatment plan. The requirements are management-system-based, meaning the standard evaluates whether the organization has defined, implemented, measured, and improved its ISMS in a verifiable and auditable manner. All evidence must be documented, accessible, and demonstrably current at the time of the ISO 27001 certification audit.
ISO 27001 requires organizations to maintain a defined set of documented information as evidence of ISMS conformance. The scope statement must clearly define the boundaries and applicability of the ISMS, including the organizational units, locations, assets, and services covered. The Information Security Policy must be authorized by top management and communicated throughout the organization. The risk assessment methodology must be documented and consistently applied, with outputs captured in a risk register that records identified risks, likelihood, impact, risk owners, and treatment decisions. The risk treatment plan must link each accepted residual risk to specific Annex A controls or justified exclusions.
The Statement of Applicability (SoA) is a mandatory document unique to ISO 27001 that lists all 93 Annex A controls, states whether each control is applicable or excluded, provides justification for any exclusions, and references the implementation status of applicable controls. The SoA is reviewed during the ISO 27001 audit as a primary reference document linking risk treatment decisions to specific controls. Additional required documentation includes internal audit records, management review minutes, evidence of competence for personnel with information security responsibilities, corrective action records, and monitoring and measurement results. Danish organizations operating across multiple offices or jurisdictions must ensure that documentation reflects all in-scope locations.
Beyond documentation, ISO 27001 compliance requires demonstrable operational implementation of controls across the organization’s technology environment, workforce practices, and physical infrastructure. For Danish SaaS providers and cloud companies, this typically includes documented access management procedures, encryption standards, vulnerability management processes, and incident response plans that have been tested and reviewed. For pharmaceutical and healthcare organizations, controls addressing data classification, third-party processor management, and business continuity must reflect the specific sensitivity and regulatory context of patient and clinical trial data. The ISO 27001 audit evaluates whether controls are not only documented but actively applied — through testing, personnel interviews, log review, and direct observation.
ISO/IEC 27001:2022 introduced specific new requirements that Danish organizations must address in their operational implementation. Clause 6.3 now formally requires organizations to plan and manage changes to the ISMS. Annex A control A.5.7 (Threat Intelligence) requires organizations to collect and analyze information about threats relevant to their assets. A.8.11 (Data Masking) and A.8.12 (Data Leakage Prevention) introduce data protection controls at the technical layer. Organizations must demonstrate that these newly introduced controls have been evaluated during risk assessment and either implemented with documented rationale or explicitly excluded in the Statement of Applicability with justified reasoning. ISMS certification evaluators will verify the completeness and consistency of this control mapping during the ISO 27001 certification audit.
ISO 27001 is a management system standard, which means it places specific requirements on organizational leadership and governance structures. Top management must demonstrate active involvement in the ISMS — not merely nominal sponsorship — by establishing the information security policy, assigning roles and authorities, and participating in management review. The management review process must evaluate ISMS performance against defined objectives, review internal audit results, assess risk treatment outcomes, and record decisions on continual improvement actions. Evidence of management review is a mandatory audit artifact and is evaluated at both Stage 1 and Stage 2 of the ISO 27001 certification audit. Danish organizations with distributed governance structures — such as those operating subsidiaries across multiple EU countries — must ensure that management engagement is demonstrable across the full ISMS scope.
| ISO 27001 Clause | Requirement Area | Key Evidence Evaluated |
|---|---|---|
| Clause 4 | Context of the Organization | Scope statement, stakeholder analysis, interested party register |
| Clause 6 | Planning | Risk register, risk treatment plan, Statement of Applicability, security objectives |
| Clause 7 | Support | Competence records, awareness evidence, documented information inventory |
| Clause 9 | Performance Evaluation | Internal audit reports, management review minutes, KPIs and metrics |
| Clause 10 | Improvement | Nonconformity records, corrective action evidence, continual improvement log |
- ✓Mandatory Documentation Requirements
- ✓Operational and Technical ISMS Requirements
- ✓Management System Requirements
ISO 27001 Certification Audit Process in Denmark
The ISO 27001 certification audit process follows a defined sequence of stages — from initial application through certification issuance and ongoing surveillance. CertPro CPA LLC conducts ISO 27001 certification audits for Denmark-based organizations in accordance with ISO/IEC 17021-1 and ISO/IEC 27006 requirements, which govern competence, consistency, and impartiality in management system certification. Each stage of the ISO 27001 audit is evaluation-focused and evidence-based, with findings documented in formal audit reports that form the basis of the certification decision.
The Stage 1 audit — also referred to as the documentation review or ISMS readiness assessment — evaluates whether the organization’s documented ISMS is sufficiently developed to proceed to the Stage 2 certification audit. The auditor reviews the scope statement, information security policy, risk assessment methodology, risk register, risk treatment plan, and Statement of Applicability for completeness and internal consistency. The Stage 1 audit determines whether the organization understands the requirements of ISO/IEC 27001:2022, has clearly defined its ISMS boundaries, and has sufficient documentation in place to support full operational assessment. The outcome is a Stage 1 audit report identifying any significant gaps or areas requiring resolution before Stage 2 proceeds.
For Danish organizations with operations across multiple sites — for example, a Copenhagen-headquartered SaaS company with development teams in Aarhus or data center operations in Odense — the Stage 1 audit evaluates whether the ISMS scope adequately covers all included locations and functions. The auditor confirms that interested parties relevant to the Danish and EU operating context — including data subjects, regulators, enterprise customers, and cloud infrastructure providers — have been identified and their expectations considered in the ISMS design. Any observations raised during Stage 1 are communicated to the organization prior to Stage 2 scheduling, allowing the organization to address documentation deficiencies before the ISO 27001 operational audit commences.
The Stage 2 audit is the primary ISO 27001 certification audit, during which the auditor evaluates whether the organization’s ISMS is effectively implemented and operational across all in-scope areas. This audit involves structured interviews with personnel holding information security responsibilities, review of operational logs and records, examination of access control configurations, assessment of incident management records, and verification of internal audit completion. The auditor evaluates conformance with all mandatory clauses of ISO/IEC 27001:2022 and verifies that Annex A controls declared as applicable in the Statement of Applicability are demonstrably implemented. For Danish organizations in regulated sectors, the Stage 2 audit also examines how ISMS controls interact with sector-specific security requirements.
The Stage 2 ISO 27001 audit in Denmark typically requires two to five audit days depending on organizational size, ISMS scope complexity, and the number of in-scope locations. At the conclusion of the Stage 2 audit, the auditor issues an audit report documenting conformances, observations, and any nonconformities identified. Major nonconformities — defined as the absence or complete failure of a required system element — must be resolved and verified before ISO 27001 certification is issued. Minor nonconformities must be addressed within the timeframe specified by the certification body. Upon satisfactory resolution of all findings, the certification decision is made and the ISO 27001 certificate is issued for a three-year cycle.
ISO 27001 certificates are valid for three years and are subject to annual surveillance audits to verify that the ISMS remains effective and continues to conform to the standard between recertification cycles. Surveillance audits are conducted at a minimum once per year following initial certification. They are typically scoped to evaluate specific Annex A control domains, review the outcomes of internal audits and management reviews, assess the organization’s handling of any information security incidents since the previous audit, and confirm that corrective actions from prior findings have been effectively closed. For Danish organizations that have undergone material changes — such as a significant expansion of cloud infrastructure, a merger, or the addition of new service lines — the surveillance audit evaluates whether the ISMS scope and controls remain appropriate to the changed organizational context. Recertification audits at the end of the three-year cycle repeat a structured assessment similar in scope to the original Stage 2 ISO 27001 certification audit.
- ✓Stage 1 Audit: Documentation and Readiness Review
- ✓Stage 2 Audit: Operational Certification Assessment
- ✓Surveillance Audits and Recertification
ISO 27001 Annex A Controls Relevant to Danish Organizations
Annex A of ISO/IEC 27001:2022 provides a reference set of 93 information security controls organized across four control themes. Organizations do not implement all 93 controls universally — each control’s applicability is determined by the organization’s risk assessment, the nature of its information assets, its operating environment, and legal or contractual obligations. Danish organizations across different sectors apply Annex A controls in ways that reflect their specific threat exposure, customer requirements, and regulatory context. The Statement of Applicability records which controls are applicable, which are excluded, and the rationale for each decision — forming a central audit artifact during the ISO 27001 certification audit in Denmark.
Organizational and People Controls
The Organizational controls theme (A.5) contains 37 controls covering policies, roles, threat intelligence, asset management, supplier relationships, and incident management. For Danish SaaS providers and fintech companies, controls governing supplier security (A.5.19–A.5.22) are particularly relevant given the dense use of cloud infrastructure, API integrations, and third-party data processors typical in these sectors. The threat intelligence control (A.5.7) — new in the 2022 edition — requires organizations to collect and analyze threat intelligence relevant to their assets. This aligns directly with the NIS2 Directive’s obligation for organizations to maintain awareness of cyber threats relevant to their sector. The People controls theme (A.6) addresses pre-employment screening, information security awareness, confidentiality agreements, and remote working security — all directly applicable to Danish organizations with distributed or hybrid workforce arrangements.
Incident management controls under A.5.24–A.5.28 require organizations to establish and maintain documented processes for detecting, classifying, reporting, and responding to information security events. For Danish organizations operating in sectors covered by NIS2 — including digital infrastructure, financial services, and healthcare — these ISMS controls provide a structured framework that supports, though does not replace, the specific incident notification obligations imposed by the directive. During the ISO 27001 audit, evaluators examine whether incident management procedures have been tested, whether staff are trained to recognize and report incidents, and whether post-incident reviews have resulted in documented improvements to ISMS controls. Evidence of real incident handling — where incidents have occurred — is reviewed as a direct test of operational effectiveness.
Physical and Technological Controls
The Physical controls theme (A.7) addresses physical security perimeters, access to secure areas, clear desk and screen policies, and physical security monitoring — the last of which is a new control introduced in ISO/IEC 27001:2022. Danish data center operators and organizations with on-premises server infrastructure must demonstrate physical access control logs, visitor management records, and environmental monitoring evidence. Cloud-first organizations that rely entirely on third-party infrastructure must document how physical security obligations are satisfied through supplier controls and contractual arrangements — referencing supplier audit rights or third-party attestation reports as part of the ISMS evidence base. The ISO 27001 certification audit evaluates the completeness and verifiability of this evidence regardless of whether infrastructure is hosted internally or externally.
The Technological controls theme (A.8) contains 34 controls covering access rights, authentication, encryption, vulnerability management, configuration management, data masking, data leakage prevention, and secure development. For Danish pharmaceutical companies and healthcare organizations handling clinical trial data, patient records, and research datasets, controls A.8.11 (Data Masking) and A.8.24 (Use of Cryptography) are directly relevant to both information security and data protection obligations. For fintech and financial services organizations, controls addressing privileged access management (A.8.2), secure authentication (A.8.5), and network security (A.8.20–A.8.22) reflect technical expectations embedded in DORA and financial sector supervisory guidance issued by the Danish Financial Supervisory Authority (Finanstilsynet). ISMS certification auditors evaluate these controls through technical evidence review, configuration sampling, and personnel interviews.
Benefits of ISO 27001 Certification for Denmark-Based Organizations
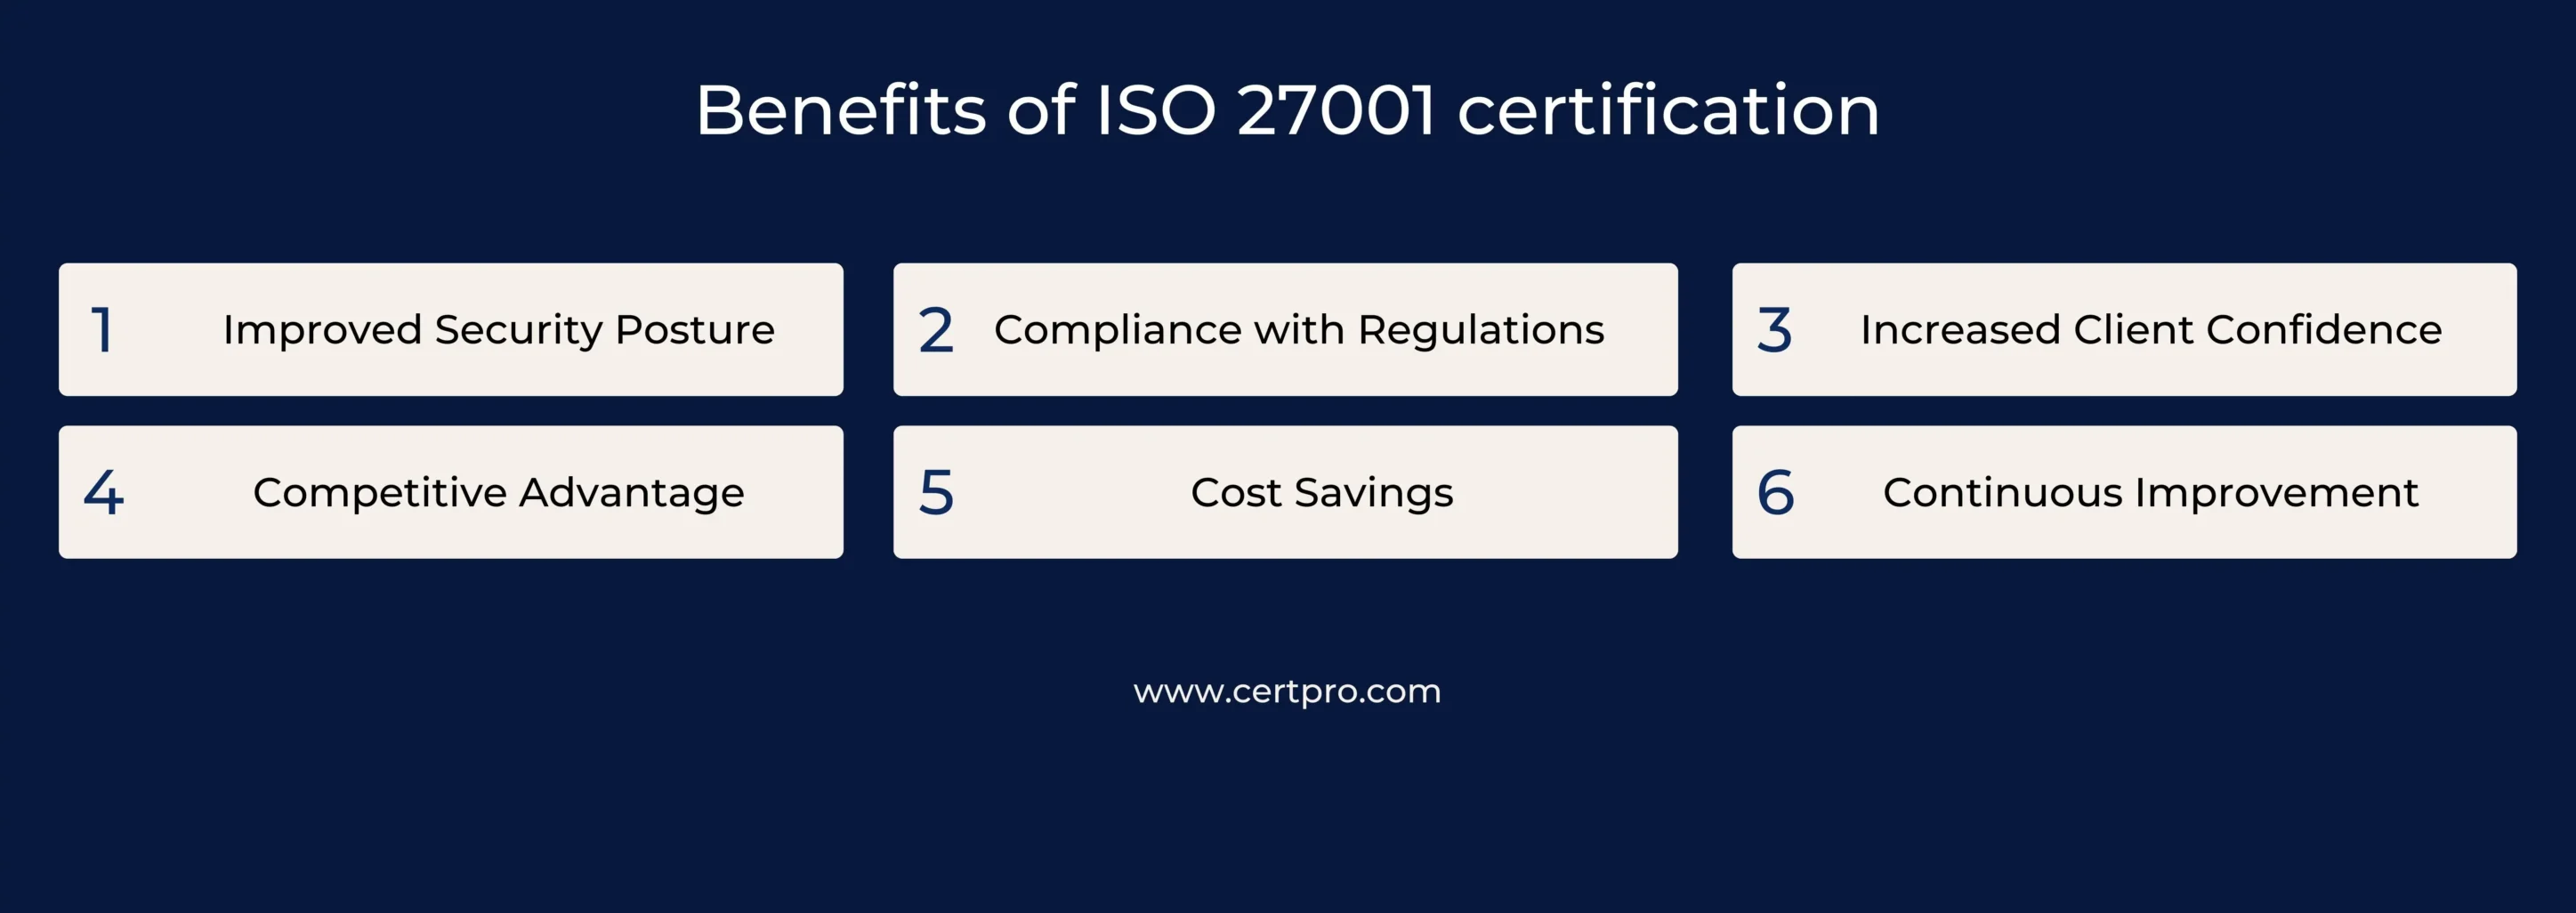
ISO 27001 Certification in Denmark delivers measurable organizational benefits that extend beyond information security management into commercial positioning, regulatory alignment, and operational governance. For Danish organizations competing in international markets, the certification mark functions as independently verified evidence of structured security governance — a qualification that self-attestation or questionnaire-based assessments cannot replicate. The following benefits represent the primary value drivers that Danish organizations in technology, financial services, healthcare, and industrial sectors commonly realize through ISMS certification.
- ✓Vendor qualification: ISO 27001 Certification is accepted as evidence of information security governance in enterprise procurement, public-sector tendering, and financial sector supplier due diligence processes across Denmark and the EU
- ✓Regulatory alignment: The ISMS framework supports documentation of technical and organizational measures required under GDPR, the Danish Data Protection Act, NIS2, and DORA — though ISO 27001 certification does not constitute legal compliance with any of these regulations
- ✓Customer assurance: Danish B2B customers, particularly in financial services and healthcare, increasingly require ISO 27001 Certification from technology vendors as a condition of data processing agreements
- ✓Cross-border market access: ISO 27001 Certification is recognized internationally, supporting Danish organizations entering markets in the EU, US, UK, and Asia-Pacific where independent third-party security attestation is expected
- ✓Incident risk reduction: Organizations with implemented and audited ISMS controls demonstrate lower rates of undetected security incidents and faster incident detection and response compared to organizations without structured information security governance
- ✓Internal governance improvement: The management review, internal audit, and corrective action cycles embedded in ISO 27001 create a continuous improvement mechanism for information security that increases organizational resilience over time
- ✓Contractual obligation fulfillment: Many Danish organizations operating as processors under GDPR data processing agreements or as suppliers under financial sector contracts include ISO 27001 certification as a contractual security requirement
- ✓Reputational differentiation: In Denmark’s SaaS, fintech, AI, and cloud sectors, ISO 27001 Certification distinguishes organizations that have undergone independent ISO 27001 audit from those that rely solely on self-declared security practices
Danish organizations subject to GDPR are required under Article 32 to implement appropriate technical and organizational measures to ensure a level of security appropriate to the risk of processing personal data. The ISO 27001 ISMS framework — with its structured risk assessment, risk treatment, control implementation, and management review processes — directly supports the documentation and operational evidence that Article 32 requires. While the Danish Data Protection Authority (Datatilsynet) does not automatically equate ISO 27001 certification with GDPR compliance, the audit evidence produced through an ISO 27001 certification audit provides a structured and independently verified record of security measures. This evidence can be presented to regulators, data subjects, and data controllers in the event of an inquiry or incident investigation.
For Danish organizations within the scope of the NIS2 Directive — including operators of essential services in energy, transport, healthcare, drinking water, digital infrastructure, and ICT service management — ISO 27001 compliance provides a structured control framework addressing many of the cybersecurity risk management measures that NIS2 Article 21 requires. Similarly, financial entities subject to DORA from January 2025 onward can reference ISO 27001 certification audit evidence as part of the ICT risk management documentation that DORA requires. In both cases, ISO 27001 certification functions as a supporting governance instrument rather than a substitute for sector-specific legal compliance obligations. Danish organizations are advised to consult legal and regulatory counsel to determine the specific compliance obligations applicable to their operations.
- ✓ISO 27001 Certification and Danish Regulatory Context
ISO 27001 Certification for Specific Danish Industry Sectors
ISO 27001 Certification in Denmark is pursued across a broad range of industry sectors, each with distinct information security drivers, threat profiles, and certification use cases. The Danish business environment encompasses globally active enterprises in pharmaceuticals, maritime technology, financial services, information technology, and telecommunications — alongside a large and growing startup and scale-up ecosystem in Copenhagen’s tech cluster, Aarhus’s digital economy, and Odense’s robotics and automation sector. Sector-specific considerations directly influence the scope, control selection, and audit focus of the ISO 27001 certification process for organizations in each industry.
Financial Services, Fintech, and ISO 27001 Compliance Denmark
ISO 27001 certification for Denmark’s financial services sector — including banks, insurance companies, payment institutions, investment firms, and fintech companies — is driven by a combination of customer expectations, regulatory requirements, and the sector’s inherent exposure to financial fraud, data theft, and systemic cyber risk. ISO 27001 compliance Denmark fintech organizations pursue certification to satisfy enterprise customer due diligence requirements, demonstrate alignment with Finanstilsynet supervisory expectations, and provide structured evidence for DORA ICT risk management documentation. The ISO 27001 certification audit for financial sector organizations typically examines access control robustness, change management processes, cryptographic key management, third-party ICT provider oversight, and business continuity planning — all areas of heightened risk in financial data environments. Copenhagen-based fintech firms and payment processors frequently reference ISO 27001 Certification in customer contracts and regulatory filings as evidence of independent security governance.
Healthcare, Life Sciences, and Pharmaceutical Organizations
Danish pharmaceutical companies, healthcare technology providers, and life sciences organizations handling clinical trial data, patient health records, and research datasets represent a significant segment of ISO 27001 certification demand in Denmark. Organizations operating in the life sciences cluster around Copenhagen and Aarhus process large volumes of sensitive personal data classified as special category data under GDPR — creating heightened obligations for technical security measures and third-party processor oversight. ISO 27001 certification provides these organizations with a structured audit framework that evaluates data classification, access control, encryption, secure research data management, and supplier security controls against a globally recognized standard. For healthcare organizations supplying digital health platforms or clinical software to hospital systems across Denmark and the EU, ISMS certification Denmark is frequently a procurement requirement embedded in tender documentation and data processing agreements.
SaaS Providers, Cloud Companies, and Technology Organizations
ISO 27001 Certification is particularly prevalent among Danish SaaS providers and cloud companies serving enterprise customers across Europe and internationally, where information security questionnaires and vendor security assessments are standard components of commercial onboarding. For SaaS organizations, the ISMS scope typically encompasses software development environments, cloud hosting infrastructure, customer data processing activities, and operational support functions. The ISO 27001 certification audit evaluates secure development practices, vulnerability management, access control for production environments, data segregation between customer tenants, and the organization’s process for managing security across the software development lifecycle. Danish AI companies and machine learning platform providers handling large datasets and proprietary model infrastructure increasingly pursue ISO 27001 Certification to satisfy the security assurance requirements of enterprise customers operating in regulated industries.
Maritime Industry and ISO 27001 Denmark
ISO 27001 Denmark maritime industry organizations — including shipping companies, port operators, maritime technology suppliers, and vessel management system providers — represent an emerging certification segment as the sector’s digital transformation increases exposure to operational technology and IT convergence risks. Danish maritime organizations that supply digital navigation systems, fleet management software, or port logistics platforms to international customers increasingly encounter ISO 27001 certification requirements in commercial contracts and flag state or port state cybersecurity frameworks. The ISO 27001 audit for maritime technology organizations typically evaluates IT/OT boundary controls, network segmentation, remote access security, and third-party supplier management for software vendors whose systems interface with vessel control infrastructure. The IMO’s Maritime Cyber Risk Management guidelines and ICS Cyber Security Guidelines reference structured ISMS frameworks consistent with ISO 27001 as appropriate mechanisms for maritime cyber risk governance.
ISO 27001 and Danish Regulatory Alignment
Danish organizations operate within a layered regulatory environment that combines national legislation with EU-level directives and sector-specific supervisory frameworks. ISO 27001 compliance in Denmark provides a structured management system approach that intersects with several of these regulatory obligations — without replacing any of them. Understanding how the ISO 27001 ISMS framework relates to each regulatory instrument is important for Danish organizations determining the role that certification plays in their overall compliance posture.
GDPR, the Danish Data Protection Act, and ISO 27001
The EU General Data Protection Regulation requires data controllers and processors to implement technical and organizational measures appropriate to the risk of their processing activities, as defined in Article 32. The ISO 27001 ISMS framework provides a systematic process for identifying information security risks, selecting and implementing controls, and maintaining documented evidence of those measures — directly addressing the accountability and security-by-design principles that GDPR requires. The Danish Data Protection Act (Databeskyttelsesloven) supplements GDPR with national provisions and is enforced by Datatilsynet, which has issued specific guidance on technical and organizational measures for data controllers and processors operating in Denmark. ISO 27001 certification audit evidence — including the risk register, Statement of Applicability, control implementation records, and incident management documentation — provides structured and independently verified material that supports accountability demonstrations to Datatilsynet. ISO 27001 certification does not, however, constitute a GDPR certification under Article 42, which requires a distinct scheme approved by a supervisory authority.
NIS2 Directive and DORA Considerations
The NIS2 Directive, transposed into Danish law through the Act on Network and Information Security (Lov om net- og informationssikkerhed), requires essential and important entities to implement risk management measures addressing network and information system security, incident handling, business continuity, supply chain security, and vulnerability disclosure. The cybersecurity risk management measures specified in NIS2 Article 21 closely parallel the ISMS control domains addressed by ISO/IEC 27001:2022 — making ISO 27001 audit evidence directly relevant to organizations demonstrating NIS2 compliance to the Danish Centre for Cyber Security (CFCS) or relevant sector supervisory authorities. ISO 27001 compliance does not automatically satisfy NIS2 obligations, but the structured documentation and audit trail generated through the ISO 27001 certification process provides a credible evidential foundation for regulatory assessments.
DORA, which applies to financial entities and their critical ICT third-party service providers from 17 January 2025, establishes specific requirements for ICT risk management, incident reporting, digital operational resilience testing, and ICT third-party risk oversight. Danish banks, investment firms, insurance companies, payment institutions, and crypto-asset service providers within DORA’s scope must maintain ICT risk management frameworks that include documented policies, incident classification procedures, and third-party oversight programs. ISO 27001 certification audit evidence in Denmark — particularly documentation of ICT risk assessments, access management controls, business continuity procedures, and supplier security evaluations — provides structured support for DORA ICT risk management documentation requirements. Organizations subject to DORA should engage legal and compliance specialists to map ISO 27001 ISMS controls to DORA’s specific regulatory technical standards.
CertPro ISO 27001 Certification Audits in Denmark
CertPro CPA LLC is a Licensed CPA Firm that conducts independent ISO 27001 certification audits for organizations operating across Denmark. CertPro evaluates ISMS conformance against ISO/IEC 27001:2022 through a structured audit methodology that encompasses Stage 1 documentation review, Stage 2 operational assessment, surveillance audits, and recertification audits. All ISO 27001 certification audit activities conducted by CertPro are evaluation-focused and evidence-based, with findings documented in formal audit reports that support the certification decision process.
Audit Methodology and Scope Evaluation
CertPro’s ISO 27001 audit methodology applies structured evaluation criteria derived from ISO/IEC 27001:2022, ISO/IEC 27006, and ISO/IEC 19011 guidelines for auditing management systems. The audit begins with scope definition, during which the auditor confirms the boundaries of the ISMS under assessment — including the information assets and processes within scope, the locations and organizational units covered, and any exclusions or limitations. For Danish organizations with multi-site operations across Copenhagen, Aarhus, Odense, and Aalborg, the auditor determines whether a representative sampling approach or full-site coverage is appropriate based on the organizational risk profile and ISMS design. Scope evaluation is documented in the audit program and forms the basis for time allocation, auditor resource planning, and interview scheduling across the ISO 27001 certification audit.
The ISO 27001 audit Denmark engagement conducted by CertPro covers all mandatory clauses of ISO/IEC 27001:2022 and evaluates the implementation status of all Annex A controls declared as applicable in the organization’s Statement of Applicability. Auditors use a combination of document review, structured interviews, technical evidence sampling, and direct observation to gather objective audit evidence. Control effectiveness is evaluated through examination of operational records — including access logs, vulnerability scan reports, change management records, security awareness training records, and incident management logs — rather than through reliance on management representations alone. The ISMS certification decision is made by a CertPro certification reviewer independent of the audit team, ensuring that the evaluation and certification decision functions are separated in accordance with impartiality requirements.
Certification Issuance and Ongoing Surveillance
Upon satisfactory completion of the Stage 2 ISO 27001 certification audit and resolution of any nonconformities identified during the process, CertPro issues the ISO 27001 certificate to the organization. The certificate specifies the certification scope, the standard version (ISO/IEC 27001:2022), the certification body, the initial certification date, and the expiry date of the three-year certification cycle. Certified organizations receive a certification mark for use in accordance with CertPro’s mark usage policy, which governs how the mark may be displayed in commercial materials, tenders, and customer-facing communications. ISO 27001 certification is maintained through annual surveillance audits and renewed through a full recertification audit at the end of the three-year cycle — ensuring that ISMS certification in Denmark remains current and reflects the organization’s ongoing operational reality.
FAQ
▶
What is ISO 27001 certification?
▶
What is ISO 27001 Certification?
▶
Is ISO 27001 Certification mandatory in Denmark?
▶
How long does the ISO 27001 audit process take for a Danish organization?
▶
What is the Statement of Applicability in ISO 27001?
▶
Does ISO 27001 Certification demonstrate GDPR compliance?
▶
How often are surveillance audits conducted after ISO 27001 certification?
▶
What is the difference between ISO 27001 and ISO 27002?



Get In Touch
have a question? let us get back to you.