
SOC 2 Certification in Indiana
SOC 2 Certification in Indiana is issued exclusively by a Licensed CPA Firm following a formal, independent examination conducted under AICPA AT-C Section 205 attestation standards. The SOC 2 certification process evaluates an organization’s control environment against the Trust Services Criteria, producing an evidence-based attestation report that verifies whether controls were suitably designed and — for Type 2 examinations — operated effectively across a defined observation period.
OUR CLIENTS










Independent SOC 2 Certification by a Licensed CPA Firm in Indiana
SOC 2 Certification in Indiana is performed exclusively by a Licensed CPA Firm acting as an independent attestation body under AICPA AT-C Section 205 standards. The SOC 2 certification process involves a structured examination of the organization’s control environment, with controls evaluated against the AICPA Trust Services Criteria (TSC) governing security, availability, processing integrity, confidentiality, and privacy.
The certification decision is made independently by the licensed attestation body and is not influenced by the organization under review. Indiana organizations in healthcare technology, financial services, SaaS, cloud computing, insurance technology, logistics, and advanced manufacturing pursue SOC 2 attestation to satisfy enterprise vendor due diligence requirements, regulatory supply-chain expectations, and cross-border client security requirements.
The Role of a Licensed CPA Firm in SOC 2 Attestation
SOC 2 attestation is a formal professional service regulated under AICPA standards and may only be performed by a Licensed CPA Firm with appropriate attestation qualifications. This requirement distinguishes SOC 2 certification from internal compliance assessments, vendor-managed programs, or self-declared security certifications.
The Licensed CPA Firm conducts an independent examination, evaluates evidence, and issues a formal attestation report that carries professional and legal standing. In Indiana, the licensed attestation body applies AICPA AT-C Section 205 standards throughout the SOC 2 examination, ensuring the resulting report meets evidentiary requirements expected by enterprise clients, regulated industries, and procurement professionals.
The independence requirement is fundamental to the value of SOC 2 certification. A Licensed CPA Firm conducting a SOC 2 examination must maintain independence from the organization being examined. This means the attestation body cannot simultaneously provide implementation, consulting, or advisory services to the same client during the same engagement period.
This independence requirement ensures that the resulting SOC 2 attestation report reflects objective, evidence-based findings rather than internally managed conclusions. Indiana organizations seeking SOC 2 compliance rely on this independence as the foundation of third-party credibility when presenting attestation reports to enterprise clients, regulators, and partners.
Trust Services Criteria and AICPA Attestation Standards
The AICPA Trust Services Criteria (TSC) form the evaluative framework applied during a SOC 2 examination. The Security criterion — also called the Common Criteria — is mandatory for all SOC 2 engagements. It addresses logical and physical access controls, system operations, change management, and risk mitigation.
Additional criteria — Availability, Processing Integrity, Confidentiality, and Privacy — are included in the SOC 2 examination scope based on the nature of the organization’s service commitments and the types of data it processes. Indiana-based SaaS providers typically include Security and Availability criteria, while healthcare technology firms and insurtech companies frequently add Confidentiality and Privacy to address the sensitivity of patient and policyholder data.
Each Trust Services Criterion contains a set of point-of-focus requirements that an organization’s controls must address. During the SOC 2 examination, the Licensed CPA Firm maps each relevant control to the applicable TSC requirements, evaluates control design, and — in a Type 2 engagement — tests operating effectiveness across the observation period.
The attestation report documents the scope, applicable criteria, management’s system description, the auditor’s findings, and any identified exceptions. This structured report format is widely recognized across enterprise procurement processes throughout Indiana and nationally, providing a standardized basis for vendor security evaluations.
Indiana Regulatory Context and Cross-Border Compliance Scenarios
Indiana’s regulatory environment includes several frameworks that intersect with SOC 2 compliance requirements. Indiana Code Title 24, Article 4.9 governs data breach notification obligations for organizations handling personal information of Indiana residents. Indiana’s Insurance Data Security Law, modeled after the NAIC model law, imposes specific cybersecurity program requirements on insurance licensees operating in the state.
Healthcare organizations subject to HIPAA face additional security rule requirements that align substantially with the AICPA Trust Services Criteria. SOC 2 attestation in Indiana provides a recognized mechanism for demonstrating control effectiveness across these overlapping regulatory requirements, though a SOC 2 report does not itself constitute regulatory compliance documentation.
Cross-border compliance scenarios are increasingly relevant for Indiana organizations with international operations or clients. A Carmel-based SaaS provider servicing European enterprise clients, for example, may face procurement requirements from U.S.-based customers expecting SOC 2 attestation and EU-based customers requiring evidence of GDPR-aligned data protection controls.
The Privacy criterion within the SOC 2 Trust Services Criteria addresses data collection, use, retention, disclosure, and disposal consistent with privacy commitments — providing a framework that supports cross-border vendor evaluations. SOC 2 Certification in Indiana, obtained through a Licensed CPA Firm examination, is recognized across North American and international enterprise procurement processes, supporting market access well beyond Indiana’s geographic boundaries.

SOC 2 Certification Audit Process in Indiana
The SOC 2 audit process in Indiana follows a structured sequence of stages governed by AICPA AT-C Section 205 attestation standards. Each stage of the SOC 2 examination produces documented outputs that contribute to the final attestation report. The process is designed to ensure the Licensed CPA Firm’s findings are evidence-based, independently derived, and reflective of the organization’s actual control environment during the examination period.
Understanding the SOC 2 audit process enables Indiana organizations to engage with the examination efficiently and to set accurate expectations regarding documentation requirements, timelines, and reporting outputs.
| Audit Stage | Key Activities | Output |
|---|---|---|
| Scope Definition | Identification of applicable Trust Services Criteria, system boundaries, and organizational units in scope | Defined audit scope and system description |
| Stage 1 – Documentation Review | Review of management’s system description, control documentation, and policy framework against TSC requirements | Documented findings on description completeness and control design |
| Stage 2 – Control Testing | Evidence collection, control walkthroughs, inquiry, observation, and inspection procedures across the observation period | Control testing workpapers and exception log |
| Nonconformity Review | Evaluation of identified exceptions, materiality assessment, and management response review | Exception findings and auditor conclusions |
| Attestation Report Issuance | Independent opinion formulation, certification committee review, and formal SOC 2 report issuance | Signed SOC 2 Type 1 or Type 2 attestation report |
Scope definition is the foundational stage of the SOC 2 audit process and determines the boundaries of the examination. During this stage, the Licensed CPA Firm works with management to establish which Trust Services Criteria apply, which organizational units and systems fall within the examination boundary, and which subservice organizations or third-party components require consideration.
The scope boundary directly affects which controls will be evaluated and the assertions management will make in the system description. Indiana organizations with distributed infrastructure across Indianapolis headquarters, regional data centers, and cloud service providers must carefully define subservice organization relationships to ensure the system description accurately represents the full service environment.
Management’s description of the system is a critical component of the SOC 2 examination. The description must accurately represent the services provided, the infrastructure components in scope, the software and data involved, the procedures governing operations, and the personnel responsible for executing controls. The Licensed CPA Firm evaluates whether the description fairly presents the system as designed and operated.
Inaccuracies or omissions in the system description may result in qualified findings in the attestation report. Indiana-based organizations pursuing SOC 2 Certification — including technology companies, SaaS platforms, and managed service providers — should ensure the system description encompasses all components that could materially affect the delivery of services subject to the Trust Services Criteria.
Stage 1 of the SOC 2 audit involves the Licensed CPA Firm’s review of the organization’s documentation framework against the requirements of the applicable Trust Services Criteria. The auditor examines information security policies, access control procedures, change management documentation, incident response plans, vendor management policies, and other control-related documents.
The purpose of this stage is to evaluate whether the documented control framework is sufficiently designed to address each applicable Trust Services Criterion and whether management’s system description is complete and accurate. Stage 1 findings inform the audit program for Stage 2 control testing, identifying areas where documentation requires clarification or supplementation before evidence collection proceeds.
During Stage 1 of the SOC 2 audit, the Licensed CPA Firm also evaluates the organization’s control environment at a high level — assessing risk assessment processes, governance structures, and management’s commitment to the control framework. This evaluation helps the auditor determine the nature, timing, and extent of testing procedures required in Stage 2.
For Indiana organizations pursuing SOC 2 certification for the first time, Stage 1 findings frequently identify documentation gaps that management must address before Stage 2 testing begins. The Stage 1 output also informs whether the engagement proceeds as a Type 1 or Type 2 SOC 2 examination and establishes the basis for the detailed control testing program.
Stage 2 of the SOC 2 examination involves detailed control testing through inquiry, observation, inspection of documentation, and re-performance procedures. For a SOC 2 Type 1 examination, the auditor evaluates whether controls are suitably designed as of a specific date. For a SOC 2 Type 2 examination, the auditor tests both design adequacy and operating effectiveness across the observation period — typically a minimum of six months for initial engagements and twelve months for subsequent annual cycles.
Evidence collected during Stage 2 includes system-generated reports, access logs, change management records, incident reports, vendor assessment documentation, and personnel training records. The observation period is the defined timeframe during which the organization’s controls are evaluated for consistent, effective operation.
Evidence collection procedures in the SOC 2 examination are designed to provide the Licensed CPA Firm with sufficient, appropriate evidence to support the attestation opinion. The auditor applies professional judgment when determining sample sizes, testing frequencies, and the mix of substantive and control-based testing procedures.
For Indiana organizations with high transaction volumes or complex cloud architectures — such as Indianapolis-based fintech platforms or Fort Wayne logistics technology providers — the auditor may apply automated evidence collection techniques and continuous monitoring review to assess control consistency across the observation period. The completeness and reliability of evidence directly affects the conclusions reached in the SOC 2 attestation report.
Following Stage 2 testing, the Licensed CPA Firm reviews identified exceptions or nonconformities to determine their nature, cause, and potential impact on the attestation opinion. Exceptions may arise from control design deficiencies, instances of control failure during the observation period, or inaccuracies in management’s system description.
The auditor evaluates whether identified exceptions are isolated occurrences or systemic issues and assesses their materiality in the context of the applicable Trust Services Criteria. Management’s written response to identified exceptions is incorporated into the SOC 2 attestation report, providing context and explaining corrective actions taken. The nonconformity review stage is a structured, evidence-based process that informs the auditor’s independent opinion.
The SOC 2 attestation report is issued upon completion of the examination and review process. The report includes the Licensed CPA Firm’s independent opinion, management’s assertion regarding the system description and control effectiveness, the detailed description of the system in scope, the applicable Trust Services Criteria, and the auditor’s findings for each control tested.
For SOC 2 Type 2 reports, the report also includes the observation period, testing procedures applied, and any exceptions noted. The attestation report is the formal output of the SOC 2 examination and serves as the primary document provided to customers, business partners, and procurement teams conducting vendor security evaluations. Indiana organizations typically share their SOC 2 attestation reports under confidentiality agreements with qualified parties.
- ✓Scope Definition and System Description
- ✓Stage 1 – Documentation Review and Readiness Assessment
- ✓Stage 2 – Control Testing and Evidence Collection
- ✓Nonconformity Review and Attestation Report Issuance
SOC 2 Type 1 vs. SOC 2 Type 2 Examination in Indiana
SOC 2 examinations in Indiana are conducted under two distinct report structures: Type 1 and Type 2. Understanding the difference between these examination types is essential for Indiana organizations determining which report structure aligns with their customer requirements, regulatory expectations, and operational readiness.
Both report types are issued by a Licensed CPA Firm following an independent examination, and both constitute formal SOC 2 attestation under AICPA standards. However, they differ significantly in scope, observation period, and the level of assurance provided to report recipients.
SOC 2 Type 1 Examination — Design Adequacy at a Point in Time
A SOC 2 Type 1 examination evaluates whether an organization’s controls are suitably designed to meet the applicable Trust Services Criteria as of a specific date. The Type 1 report does not assess whether controls operated effectively over a period of time — it addresses the design of the control environment at a single point. Type 1 examinations are appropriate for organizations that have recently implemented their control frameworks and seek formal SOC 2 attestation of design adequacy before committing to the extended observation period required for a Type 2 report.
SOC 2 Type 1 examinations in Indiana are commonly pursued by early-stage SaaS companies, newly formed technology ventures, or organizations entering regulated markets for the first time.
The Type 1 report provides a foundational level of assurance that the organization has implemented a control framework aligned with the AICPA Trust Services Criteria. While Type 1 reports are valued by some enterprise procurement teams as an initial indicator of security posture, many large financial institutions, healthcare systems, and government contractors require a SOC 2 Type 2 report before approving vendor relationships.
Indiana organizations pursuing SOC 2 Certification for the first time frequently begin with a Type 1 examination to establish an attestation baseline, then transition to annual Type 2 examination cycles. A Type 1 report is not a prerequisite for a Type 2 engagement, though this sequential approach is common.
SOC 2 Type 2 Examination — Operating Effectiveness Over an Observation Period
A SOC 2 Type 2 examination evaluates both the design adequacy and the operating effectiveness of an organization’s controls over a defined observation period — typically ranging from six to twelve months. The observation period is the timeframe during which the Licensed CPA Firm assesses whether controls operated consistently and effectively in practice, not merely whether they were designed appropriately.
The Type 2 report provides substantially higher assurance than the Type 1 report because it demonstrates sustained control performance across an extended period. This addresses the practical reality that security controls must function reliably under real-world conditions, not only at a single point in time.
SOC 2 Type 2 examinations in Indiana are the standard requirement across enterprise vendor procurement processes in the state’s healthcare technology, financial services, insurance, logistics, and advanced manufacturing sectors. A Bloomington-based healthcare IT company providing data management services to hospital systems, for example, will typically be required to provide a current SOC 2 Type 2 report as a condition of vendor approval.
Similarly, SOC 2 Certification that Indiana financial services firms require from technology vendors is almost universally structured as a Type 2 examination covering at least the Security criterion. Annual renewal of the SOC 2 Type 2 examination ensures the attestation report remains current and reflects ongoing control effectiveness, rather than a historical snapshot.
| Examination Type | Evaluation Scope | Observation Period | Common Use Case |
|---|---|---|---|
| SOC 2 Type 1 | Control design adequacy at a specific date | None — point-in-time assessment | Initial SOC 2 attestation for newly implemented controls |
| SOC 2 Type 2 | Control design and operating effectiveness over time | Minimum 6 months; typically 12 months annually | Enterprise vendor requirements and regulated industry procurement in Indiana |
| Annual Renewal | Updated Type 2 covering the subsequent 12-month period | 12-month cycle from prior report end date | Maintaining current SOC 2 attestation status for ongoing client relationships |
SOC 2 Certification Requirements and Trust Services Criteria
SOC 2 certification requirements are defined by the AICPA Trust Services Criteria and the attestation standards under which the examination is conducted. Achieving SOC 2 Certification requires an organization to demonstrate that its control environment is suitably designed — and, for Type 2 engagements, effectively operating — against each applicable Trust Services Criterion within the defined scope.
The requirements evaluated during a SOC 2 examination span technical controls, organizational policies, process documentation, personnel accountability structures, and evidence retention practices. Indiana organizations pursuing SOC 2 compliance must ensure their control frameworks address each applicable criterion comprehensively before the examination period concludes.
The Security criterion — designated as CC (Common Criteria) in the AICPA Trust Services Criteria framework — is mandatory for all SOC 2 examinations and forms the foundational control domain evaluated in every engagement. The Common Criteria are organized across nine control categories: CC1 (Control Environment), CC2 (Communication and Information), CC3 (Risk Assessment), CC4 (Monitoring of Controls), CC5 (Control Activities), CC6 (Logical and Physical Access Controls), CC7 (System Operations), CC8 (Change Management), and CC9 (Risk Mitigation).
Each category contains specific points of focus that the organization’s controls must address. During a SOC 2 audit in Indiana, the Licensed CPA Firm evaluates controls across all nine Common Criteria categories regardless of which additional Trust Services Criteria are included in scope.
Control requirements under the Security criterion include, among others: defined access control policies with least-privilege enforcement, multi-factor authentication for privileged account access, encryption of data in transit and at rest, vulnerability management programs with defined scanning frequencies and remediation timelines, security incident detection and response procedures, and regular security awareness training for personnel.
Evidence collected during the SOC 2 examination must demonstrate that these controls are not only documented in policy but consistently executed in practice. For Indiana SaaS and cloud service providers, evidence typically includes system-generated access logs, vulnerability scan reports, penetration test results, incident response records, and training completion records spanning the observation period.
The Availability criterion addresses whether the organization’s system is available for operation and use as committed or agreed. Availability controls include capacity management, system monitoring, disaster recovery procedures, backup verification, and defined recovery time and recovery point objectives. Indiana logistics technology providers and cloud infrastructure companies frequently include the Availability criterion in their SOC 2 examination scope because uptime and continuity commitments are central to their service level agreements.
Evidence for the Availability criterion includes uptime monitoring reports, disaster recovery test documentation, and backup integrity verification records.
The Processing Integrity criterion evaluates whether system processing is complete, valid, accurate, timely, and authorized. This criterion is particularly relevant for Indiana financial services organizations, payment processors, and data analytics platforms where the accuracy of processed transactions directly affects customer outcomes and regulatory compliance.
The Confidentiality criterion addresses the protection of information designated as confidential under the organization’s commitments. The Privacy criterion — the most expansive of the additional criteria — evaluates the organization’s personal information lifecycle management, including collection, use, retention, disclosure, and disposal of personal data. SOC 2 compliance that Indiana healthcare technology and insurtech organizations require often encompasses both the Confidentiality and Privacy criteria.
Evidence requirements for a SOC 2 examination are determined by the Licensed CPA Firm’s audit program and the specific controls being tested. Evidence must be sufficient, appropriate, and relevant to the control assertions being evaluated. Common categories of evidence include information security policies and procedures, access control matrix documentation, user provisioning and deprovisioning records, change management tickets and approval records, security monitoring alerts and response documentation, vendor assessment records, business continuity and disaster recovery test reports, and security training completion records.
The completeness and accuracy of evidence directly determines the auditor’s conclusions regarding control effectiveness in the SOC 2 attestation report.
- ✓Information security policies covering access control, incident response, change management, and data classification
- ✓Risk assessment documentation identifying threats, vulnerabilities, and corresponding control responses
- ✓Access control matrices and user provisioning records demonstrating least-privilege enforcement
- ✓Multi-factor authentication configuration records and exception logs
- ✓Vulnerability scan reports and penetration test results with remediation tracking documentation
- ✓Security monitoring logs, alert records, and incident response documentation spanning the observation period
- ✓Vendor and subservice organization assessment records and contractual security requirements
- ✓Business continuity and disaster recovery plans with documented testing results
- ✓Security awareness training completion records for all personnel within the SOC 2 examination scope
- ✓Change management records including testing, approval, and deployment documentation
- ✓Security Criterion — Common Criteria Requirements
- ✓Additional Trust Services Criteria — Availability, Processing Integrity, Confidentiality, Privacy
- ✓Evidence Requirements and Documentation Standards
Business Sectors in Indiana Pursuing SOC 2 Certification
SOC 2 Certification in Indiana is pursued across a broad range of industry sectors, driven by enterprise vendor security requirements, regulatory supply-chain expectations, and competitive market positioning. Indiana’s diverse economic base — encompassing healthcare and life sciences, financial services and insurance, advanced manufacturing, logistics and transportation, technology and SaaS, and growing AI and cybersecurity ecosystems — creates demand for SOC 2 attestation across organizations of varying sizes and technical profiles.
The following sections describe the primary industries driving SOC 2 certification demand within Indiana.
Healthcare Technology and Life Sciences
Indiana is home to one of the largest concentrations of life sciences and healthcare organizations in the United States, with major employers and research institutions centered in Indianapolis and Bloomington. Companies such as Eli Lilly, Roche Diagnostics, and Cook Medical — along with a substantial ecosystem of healthcare IT vendors, clinical data management platforms, and telehealth providers — generate significant demand for SOC 2 Certification in Indiana.
Healthcare technology companies providing electronic health record integrations, clinical decision support systems, patient engagement platforms, and revenue cycle management services are routinely required to provide current SOC 2 attestation reports as a condition of vendor approval by hospital systems and health plans.
For Indiana healthcare technology organizations, the SOC 2 examination typically encompasses the Security and Confidentiality criteria at minimum, with many organizations also including the Privacy criterion given the sensitivity of protected health information. The intersection of SOC 2 compliance and HIPAA Security Rule requirements creates a complementary framework where SOC 2 control testing evidence can support HIPAA risk analysis documentation.
However, SOC 2 attestation does not constitute HIPAA compliance certification, and Indiana healthcare IT vendors must maintain both compliance frameworks independently. The Privacy criterion’s alignment with HIPAA’s minimum necessary standard and data use limitation requirements makes it a natural addition to the SOC 2 examination scope for organizations handling protected health information.
Financial Services, Insurance, and Fintech
Indiana’s financial services sector includes major insurance carriers, regional banks, credit unions, investment management firms, and a growing fintech ecosystem concentrated in Indianapolis and Carmel. Organizations such as OneAmerica and numerous insurance technology startups operate in an environment where SOC 2 certification requirements are embedded in vendor procurement processes. Insurance carriers subject to Indiana’s Insurance Data Security Law must maintain documented cybersecurity programs and conduct third-party vendor risk assessments, creating direct demand for SOC 2 attestation from technology vendors serving the insurance industry.
SOC 2 compliance for Indiana fintech organizations is driven by multiple factors including banking-as-a-service partnership requirements, payment card industry expectations, and enterprise financial institution procurement standards. Fintech companies providing payment processing, lending platforms, wealth management technology, or banking infrastructure to regulated financial institutions must typically demonstrate control effectiveness through a current SOC 2 Type 2 report before entering data-sharing or system integration arrangements.
The SOC 2 examination for Indiana financial services organizations frequently includes the Security, Availability, Processing Integrity, and Confidentiality criteria, reflecting the multiple dimensions of control effectiveness relevant to financial data processing environments.
SaaS Providers, Cloud Computing, and Managed Service Providers
Indiana’s technology sector has expanded significantly across Indianapolis, Carmel, and South Bend, with a growing concentration of SaaS companies, cloud platform providers, and managed service providers serving national and international enterprise clients. SOC 2 Certification that Indiana technology companies pursue is frequently a prerequisite for entering enterprise sales cycles with Fortune 500 clients, healthcare systems, financial institutions, and government contractors.
The enterprise SaaS sales cycle increasingly includes a security review stage where procurement teams review SOC 2 attestation reports, security questionnaires, and additional due diligence documentation before approving vendor relationships.
Managed service providers (MSPs) and managed security service providers (MSSPs) operating in Indiana face particular SOC 2 demand because they operate within the control environments of their clients, creating third-party risk exposure that clients must assess and document. An MSP providing IT infrastructure management to Indiana healthcare systems or financial institutions will typically be required to maintain a current SOC 2 Type 2 report covering the Security criterion at minimum, with additional criteria determined by the nature of data the MSP accesses.
The SOC 2 attestation for MSPs also addresses subservice organization relationships, documenting the controls maintained by the MSP relative to those remaining the responsibility of client organizations.
Advanced Manufacturing, Logistics, and Transportation Technology
Indiana’s advanced manufacturing sector — anchored by automotive, aerospace, pharmaceutical, and industrial manufacturing — increasingly relies on connected operational technology, industrial IoT platforms, and supply chain management systems that process sensitive operational and commercial data. Technology vendors serving Indiana manufacturers are frequently required to demonstrate control effectiveness through SOC 2 Certification as manufacturing organizations strengthen their vendor risk management programs in response to industrial cybersecurity incidents and supply chain regulatory expectations.
Fort Wayne and Kokomo-based manufacturing technology companies, as well as national logistics platforms with Indiana operations, represent a growing segment of SOC 2 certification demand across the state.
Why Indiana Organizations Pursue SOC 2 Certification
Indiana-based organizations pursue SOC 2 Certification in Indiana for a variety of strategically important reasons rooted in enterprise procurement requirements, regulatory supply-chain expectations, and market differentiation. The SOC 2 attestation report serves as a standardized, independently verified demonstration of control effectiveness that addresses the security and trust requirements of customers, regulators, and business partners across multiple industries.
The following factors represent the primary drivers of SOC 2 certification demand among Indiana organizations.
Enterprise Vendor Security Review Requirements
Enterprise vendor procurement processes across Indiana’s major industry sectors consistently include a security assessment stage where technology vendors are required to demonstrate control effectiveness through independent attestation. Large healthcare systems such as Indiana University Health, Ascension St. Vincent, and Franciscan Health maintain formal vendor risk management programs that require technology vendors handling patient data or connecting to clinical systems to provide current SOC 2 attestation reports.
Similarly, major financial institutions operating in Indiana’s banking and insurance markets require SOC 2 Type 2 reports from SaaS vendors and technology service providers before executing data processing agreements or system integration contracts.
The enterprise vendor review process typically involves a procurement or information security team reviewing the SOC 2 report in detail — examining the examination scope, applicable Trust Services Criteria, observation period covered, and any exceptions noted. Indiana technology vendors with current SOC 2 Type 2 reports can generally navigate enterprise vendor reviews more efficiently than organizations relying solely on security questionnaire responses.
The SOC 2 attestation report provides independently verified, structured evidence of control effectiveness rather than self-assessed answers. A report covering a twelve-month observation period delivers a level of assurance that security questionnaires alone cannot replicate.
Regulatory Supply-Chain Expectations and Third-Party Risk Management
Regulatory frameworks applicable to Indiana organizations increasingly impose supply-chain security obligations that extend to the organization’s technology vendors. Indiana’s Insurance Data Security Law requires insurance licensees to include security requirements in contracts with third-party service providers and to conduct oversight of vendor security practices. HIPAA’s Security Rule requires covered entities and business associates to assess the security of third-party systems that access, process, or transmit protected health information.
The SOC 2 examination provides a recognized mechanism for Indiana-regulated organizations to satisfy third-party oversight requirements when evaluating their technology vendors.
Federal contractor requirements add another dimension to SOC 2 demand for Indiana organizations. Companies engaged in defense contracting, federal healthcare programs, or federally funded research may face Cybersecurity Maturity Model Certification (CMMC) requirements or other federal supply chain security standards. While SOC 2 attestation does not equate to CMMC certification, SOC 2 compliance examinations in Indiana demonstrate overlapping control requirements in areas such as access control, incident response, configuration management, and audit logging.
Indiana organizations navigating multiple regulatory frameworks frequently find that SOC 2 certification creates a foundation of documented, tested controls that can support multiple compliance evaluations simultaneously.
Market Access, Competitive Differentiation, and Client Trust
SOC 2 certification provides Indiana technology companies with a market access credential recognized across enterprise procurement processes nationally and internationally. Organizations that obtain SOC 2 Certification in Indiana can respond to enterprise RFPs and vendor security questionnaires with a formal attestation report, reducing the time and resource investment required to complete individual client security reviews.
In competitive technology markets where multiple SaaS or cloud vendors may offer comparable functional capabilities, a current SOC 2 Type 2 report can serve as a differentiating factor in procurement decisions where security posture is a significant evaluation criterion.
Benefits of SOC 2 Certification for Indiana-Based Organizations
SOC 2 Certification in Indiana delivers a range of independently verifiable benefits that extend across sales, operations, risk management, and regulatory compliance functions. The attestation report produced through a SOC 2 examination provides Indiana organizations with an objective, evidence-based demonstration of control effectiveness that supports enterprise customer relationships, regulatory due diligence, and ongoing security program governance.
The following benefits represent the primary value delivered through formal SOC 2 attestation for Indiana-based organizations.
- ✓Independent third-party verification that security controls are suitably designed and operating effectively, as confirmed by a Licensed CPA Firm conducting a formal SOC 2 examination
- ✓Formal SOC 2 attestation report recognized across enterprise procurement processes in Indiana’s healthcare, financial services, insurance, SaaS, and manufacturing sectors
- ✓Structured evidence of control effectiveness covering the Security, Availability, Processing Integrity, Confidentiality, and Privacy Trust Services Criteria as applicable to the organization’s services
- ✓Demonstrated SOC 2 compliance with AICPA Trust Services Criteria supporting vendor security review responses and RFP requirements
- ✓Support for regulatory supply-chain oversight obligations under Indiana’s Insurance Data Security Law, HIPAA Security Rule, and other applicable frameworks
- ✓Annual SOC 2 examination cycle providing ongoing assurance of control effectiveness and continuous monitoring discipline
- ✓Market access credential supporting enterprise sales cycles, cross-border client requirements, and international vendor evaluations
- ✓Structured audit methodology that identifies control gaps through the evidence-based SOC 2 examination process, generating documented findings reviewed by management
- ✓Reduced burden on enterprise procurement and information security teams reviewing vendor security posture, accelerating vendor approval timelines
- ✓Foundation for multi-framework compliance programs addressing SOC 2, HIPAA, ISO 27001, NIST CSF, and other applicable standards with overlapping control requirements
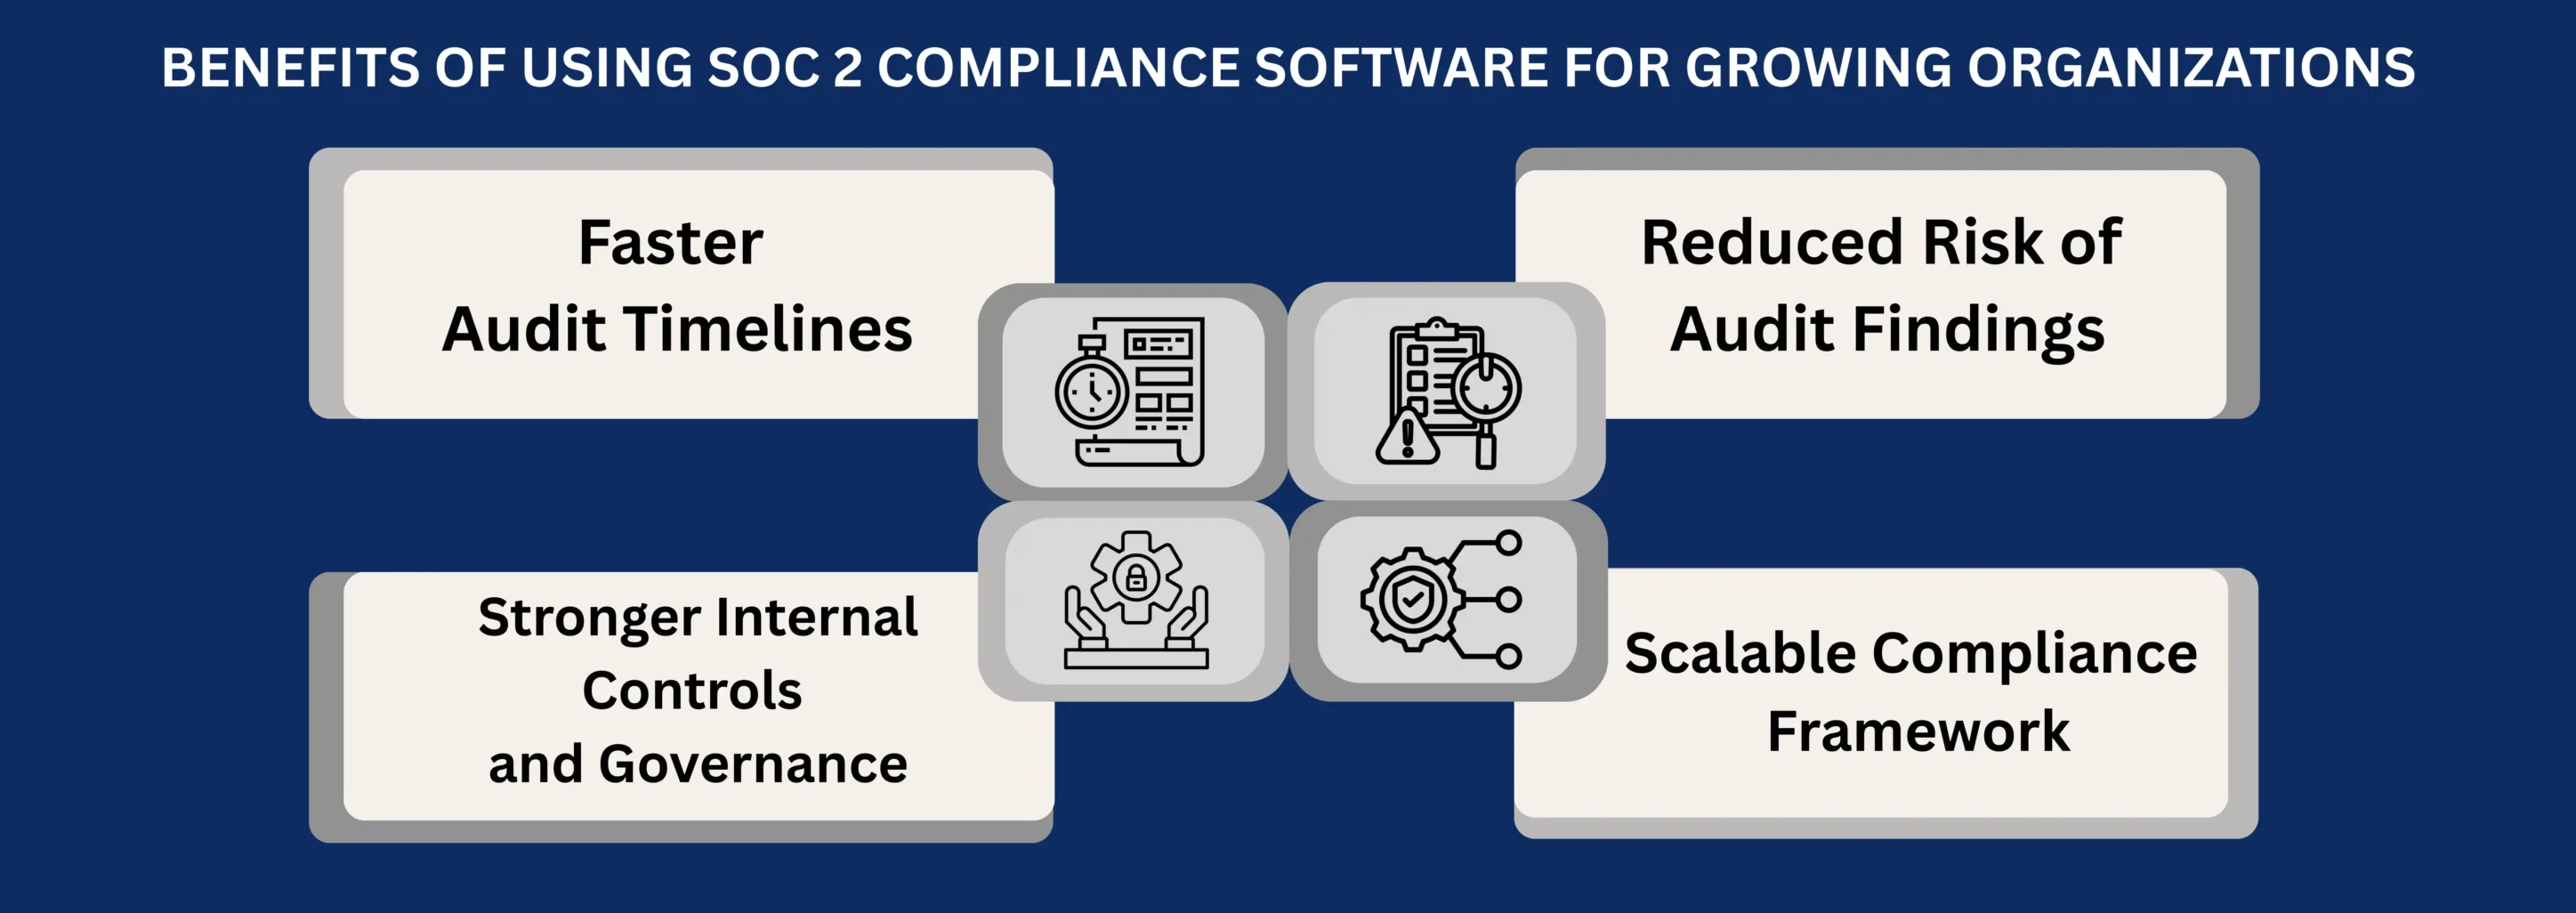
The SOC 2 examination process imposes a structured discipline on the organization’s control environment that extends beyond the audit period itself. Organizations maintaining SOC 2 compliance must sustain the documentation, evidence collection, and control monitoring practices required to support annual examination cycles. This ongoing operational discipline — encompassing regular access reviews, vulnerability scanning, security training, incident response testing, and vendor oversight — creates a continuously maintained security program rather than a periodic compliance exercise.
For Indiana SaaS and cloud providers, this operational structure supports both the SOC 2 attestation requirement and the broader security expectations of enterprise customers.
The recertification cycle associated with SOC 2 attestation ensures that control effectiveness is evaluated against an updated observation period annually. Unlike certifications that permit multi-year renewal without intervening assessments, the SOC 2 Type 2 examination cycle requires annual evidence collection, control testing, and attestation report issuance to maintain current certification status.
Indiana organizations must complete annual SOC 2 examination cycles to maintain current certified status and meet customer expectations for up-to-date attestation documentation. Enterprise clients and regulated industry procurement teams typically require SOC 2 reports covering observation periods ending within the prior twelve months, making annual cycle completion a practical necessity for organizations serving these markets.
- ✓Operational Discipline and Control Monitoring
SOC 2 Certification vs. Other Security Frameworks in Indiana
Indiana organizations evaluating their security attestation options frequently compare SOC 2 certification against other recognized frameworks including ISO 27001, NIST Cybersecurity Framework (CSF), HITRUST CSF, PCI DSS, and SOC 1. Each framework addresses distinct control objectives, is governed by different standard-setting bodies, and is recognized by different customer and regulatory audiences.
Understanding the differences between these frameworks enables Indiana organizations to determine which attestation is most relevant to their specific customer requirements and regulatory obligations.
SOC 2 vs. ISO 27001
SOC 2 and ISO 27001 are the two most commonly compared security attestation frameworks in the U.S. technology market. SOC 2 is governed by the AICPA and is exclusively performed by a Licensed CPA Firm under U.S. attestation standards. ISO 27001 is an international standard governed by the International Organization for Standardization and is certified by accredited ISO certification bodies globally.
SOC 2 attestation produces a detailed report documenting specific control testing findings against the Trust Services Criteria, while ISO 27001 certification produces a certificate confirming that the organization’s Information Security Management System conforms to the ISO/IEC 27001 standard.
For Indiana technology companies serving predominantly U.S.-based enterprise clients, SOC 2 certification is typically the primary requirement, as U.S. enterprise procurement teams are familiar with the SOC 2 report format and its evidentiary value. ISO 27001 certification is more commonly required by European enterprise clients and organizations with significant international operations.
Indiana organizations with both U.S. and international client bases may pursue both SOC 2 and ISO 27001 certifications to satisfy the different attestation expectations of their respective customer segments. The AICPA has developed mapping documentation between the Trust Services Criteria and ISO/IEC 27001, which supports organizations maintaining both certifications with overlapping evidence and control structures.
| Framework | Governing Body | Report / Certificate Type | Primary Market Recognition |
|---|---|---|---|
| SOC 2 | AICPA | SOC 2 Attestation Report (Type 1 or Type 2) | U.S. enterprise, healthcare, financial services |
| ISO 27001 | ISO / IEC | Certification Certificate | Global enterprise, European markets |
| HITRUST CSF | HITRUST Alliance | HITRUST Assessment Report | U.S. healthcare industry |
| PCI DSS | PCI Security Standards Council | Report on Compliance / Attestation of Compliance | Payment card processing environments |
SOC 2 vs. SOC 1
SOC 1 and SOC 2 are both attestation reports issued by a Licensed CPA Firm under AICPA standards, but they address fundamentally different control objectives. A SOC 1 examination evaluates controls relevant to a user entity’s financial reporting — meaning controls are assessed in terms of their potential impact on the financial statements of the organization’s customers. SOC 1 is appropriate for service organizations such as payroll processors, fund administrators, and data center operators whose services directly affect client financial reporting.
SOC 2 addresses controls relevant to security, availability, processing integrity, confidentiality, and privacy, and is appropriate for technology service providers whose services are evaluated based on operational trust rather than financial reporting impact.
Indiana organizations that process financial transactions or maintain financial records on behalf of clients — such as payroll platforms, accounting SaaS providers, or fund administration services — may need to consider whether a SOC 1 or SOC 2 report is appropriate for their specific service commitments, or whether both report types are required. Some Indiana financial technology organizations maintain both SOC 1 and SOC 2 examinations to address the financial reporting controls expected by their clients’ external auditors and the security controls expected by their clients’ procurement and information security teams.
The SOC 2 examination Indiana organizations typically pursue is distinct from the SOC 1 engagement and requires different control scope and evidence collection procedures.
SOC 2 Report Validity, Maintenance, and Recertification in Indiana
SOC 2 attestation reports do not carry indefinite validity. The report covers a specific examination period — a point in time for Type 1 reports, or a defined observation period for Type 2 reports — and reflects the organization’s control environment during that specific timeframe. Enterprise clients and regulated industry procurement teams expect current SOC 2 reports, typically requiring that the observation period of a Type 2 report has ended within the prior twelve months.
Indiana organizations with active enterprise customer relationships must maintain a continuous cycle of SOC 2 examinations to ensure that current, unqualified attestation reports remain available for client due diligence and procurement review purposes.
Annual Examination Cycle and Report Currency
The standard SOC 2 annual examination cycle for Indiana organizations involves initiating a new Type 2 engagement covering the twelve-month period following the end date of the prior report’s observation period. Organizations that allow gaps between successive examination periods may face a situation where no current SOC 2 attestation is available for client review, potentially affecting contract renewal or new client onboarding processes.
Enterprise procurement teams reviewing SOC 2 reports evaluate the observation period end date carefully. Reports covering periods ending more than twelve months prior may be considered stale for active vendor due diligence purposes.
The recertification SOC 2 examination follows the same structural stages as the initial engagement — including scope confirmation, documentation review, control testing across the new observation period, and attestation report issuance by the Licensed CPA Firm. Changes in the organization’s system, infrastructure, personnel, or service commitments between examination cycles must be documented and reflected in the updated system description.
Material changes — such as significant cloud platform migrations, major application deployments, or substantial shifts in data processing scope — may require scope adjustment in the recertification examination to ensure the SOC 2 attestation report accurately reflects the current control environment. Annual SOC 2 cycles in Indiana are typically structured to align with the organization’s fiscal year or the anniversary of the prior report’s observation period end date.
Suspension and Withdrawal of SOC 2 Attestation
Unlike ISO certification, SOC 2 attestation does not involve a formal suspension or withdrawal mechanism in the same sense. The SOC 2 attestation report represents a historical finding covering a specific period and does not carry forward ongoing validity that can be administratively revoked. However, the practical equivalent of attestation suspension occurs when an organization’s most recent SOC 2 report covers an observation period that enterprise clients consider outdated, or when a subsequent examination results in a qualified opinion indicating material control failures.
Organizations that fail to initiate timely recertification examinations effectively lose the market credibility that current SOC 2 Certification in Indiana provides in enterprise procurement processes.
Material control deficiencies discovered during a SOC 2 examination may result in a qualified attestation opinion, meaning the Licensed CPA Firm identifies one or more instances where controls did not operate effectively during the observation period. Qualified opinions are documented in the attestation report and are visible to enterprise clients reviewing the report.
Indiana organizations that receive qualified SOC 2 reports must communicate findings and their management response to clients, and typically must address underlying control deficiencies before the subsequent examination to avoid repeated qualification. The transparency of the SOC 2 report format — which documents both auditor findings and management’s responses — provides enterprise clients with detailed insight into the organization’s control environment that self-assessments cannot replicate.
Selecting a Licensed CPA Firm for SOC 2 Examination in Indiana
Selecting a Licensed CPA Firm to conduct a SOC 2 examination is a significant decision for Indiana organizations. The quality, credibility, and market recognition of the resulting SOC 2 attestation report depends on the professional standing and attestation experience of the issuing firm. SOC 2 examinations may only be performed by a CPA firm with the appropriate attestation authorization under AICPA standards, but the scope of experience and industry expertise varies significantly among firms.
Indiana organizations should evaluate several criteria when selecting a Licensed CPA Firm for their SOC 2 audit.
Independence, Qualifications, and Attestation Experience
The Licensed CPA Firm conducting the SOC 2 examination must maintain independence from the organization being examined, as required by AICPA independence standards. This independence requirement prohibits the attestation firm from simultaneously providing implementation, consulting, or advisory services to the same organization for the same engagement scope. Indiana organizations should verify the attestation firm’s independence before engagement and obtain documentation confirming that independence is maintained throughout the SOC 2 examination period.
Firms that offer both SOC 2 examination services and security consulting services must implement appropriate internal controls to segregate these activities and maintain independence between engagement teams.
Industry-specific attestation experience is a relevant differentiator among Licensed CPA Firms conducting SOC 2 examinations. A firm with extensive experience examining healthcare technology organizations understands the intersection of AICPA Trust Services Criteria with HIPAA Security Rule requirements, the typical evidence types generated by clinical information systems, and the control frameworks relevant to healthcare data processing environments.
Similarly, a firm experienced in financial services SOC 2 examinations brings knowledge of relevant regulatory requirements, payment processing control standards, and the evidence expectations of financial institution procurement teams. Indiana organizations should evaluate the relevant industry experience of prospective attestation firms when selecting a provider for their SOC 2 audit.
Report Quality and Enterprise Acceptance
The quality and completeness of the SOC 2 attestation report directly affects its acceptance by enterprise client procurement and information security teams. A well-structured SOC 2 report includes a comprehensive system description, clearly mapped controls to Trust Services Criteria points of focus, detailed testing procedures for each control, and clearly documented findings including any exceptions noted.
Enterprise clients reviewing SOC 2 reports evaluate the depth and specificity of control testing documentation — not merely the overall opinion. Indiana technology organizations should request sample reports from prospective Licensed CPA Firms and evaluate the report structure, control testing specificity, and overall documentation quality before making an engagement selection.
FAQ
▶
What is SOC 2 Certification in Indiana and who issues it?
▶
What is the difference between a SOC 2 Type 1 and Type 2 report?
▶
Which Trust Services Criteria should Indiana organizations include in their SOC 2 examination?
▶
How long is the observation period for a SOC 2 Type 2 examination in Indiana?
▶
What does SOC 2 compliance mean for Indiana organizations?
▶
Is SOC 2 certification required by law in Indiana?
▶
How does the SOC 2 examination process work for Indiana organizations?
▶
What industries in Indiana most commonly require SOC 2 certification from vendors?
SOC 1 VS SOC 2: WHICH REPORT YOUR CUSTOMERS ACTUALLY ASK FOR
If you sell SaaS or provide outsourced services, you have likely been asked for a SOC report. However, the follow-up question is rarely easy to answer…
AICPA Issues New Guidance for Peer Reviewers Evaluating SOC 2 Engagements
AICPA SOC 2 guidance has been issued to help peer reviewers identify quality risks associated with SOC 2 engagements as the use of compliance automati…
SOC 2 Certified: What Does It Mean for Your Business
For companies that handle sensitive data or run cloud-based services, the question “Can you provide your SOC 2 report?” carries enormous weight. Yet, …
Get In Touch
have a question? let us get back to you.