A SOC 2 report is a formal attest document — the written output of an examination conducted by a licensed, independent CPA firm under AICPA attestation standards. Its content is determined by evidence gathered during the engagement, not by a form someone filled out. No downloadable SOC 2 report template can replicate that, because the value of the report is inseparable from the independence and professional standing of the CPA firm that issues it.
Every month, thousands of technology companies search for a SOC 2 report template — a downloadable document they can fill in, brand with their logo, and hand to prospects. The search always ends the same way: with illustrative samples from compliance software vendors, annotated PDFs labeled 'example,' and a quiet realization that none of them will satisfy a demanding enterprise buyer.
That outcome is not a gap in the market. It reflects how a SOC 2 report actually works. A SOC 2 report is a formal attest document — the written output of an examination conducted by a licensed, independent CPA firm under AICPA attestation standards. Its content is determined by evidence gathered during the engagement, not by a form someone filled out. No downloadable SOC 2 report template can replicate that, because the value of the report is inseparable from the independence and professional standing of the CPA firm that issues it.
This article explains exactly why no legitimate SOC 2 report template exists for download, what an actual issued report contains, and what CertPro — a licensed CPA firm — provides as an independent attestation provider.
Concern
Technology vendors searching for a SOC 2 report template to download often discover that no fill-in-the-blank version carries any attestation value — yet dozens of sites offer PDFs that look official, creating real confusion about what customers and prospects will accept.
Overview
A SOC 2 report is a formal attest document issued under AICPA professional standards (AT-C Sections 205 and 320) exclusively by a licensed, independent CPA firm. Its content is determined by the auditor's examination findings — not by a template.
Solution
Organizations seeking a SOC 2 report must engage an independent CPA firm to conduct the examination. CertPro, a licensed CPA firm, performs SOC 2 examinations and issues the formal attest reports that customers, prospects, and regulators actually require.
What a SOC 2 Report Actually Is — and Why a Template Cannot Replace It
A SOC 2 report is an attest document issued under AICPA AT-C Section 205 (for Type 1) and AT-C Section 320 (for Type 2). These professional standards define the form and content of the report, the evidence requirements the CPA must satisfy, and the independence rules that make the opinion credible (Source: AICPA). Because the report is the auditor's professional opinion — not the client's self-assessment — it cannot originate from a template the client downloads and completes.
The distinction matters legally. When a customer asks for your SOC 2 report, they are asking for an attest document signed by a licensed CPA who examined your controls and is prepared to stand behind that opinion professionally. A templated or self-authored document does not satisfy that request, regardless of how accurately it describes your systems.
What vendors label a 'SOC 2 report template' or 'SOC 2 report download' online is almost always an illustrative sample — an anonymized or fictional report produced for educational purposes. These samples are useful for understanding report structure. They have no attestation value. Sharing one with a customer as though it were your issued report would misrepresent your compliance posture and could expose your organization to contractual and reputational risk.
The SOC 2 report template search problem, in short, is a terminology problem: people searching for a template are usually trying to understand what a finished report looks like, not trying to forge one. The right answer to that search is an explanation of report structure — which the next section provides.
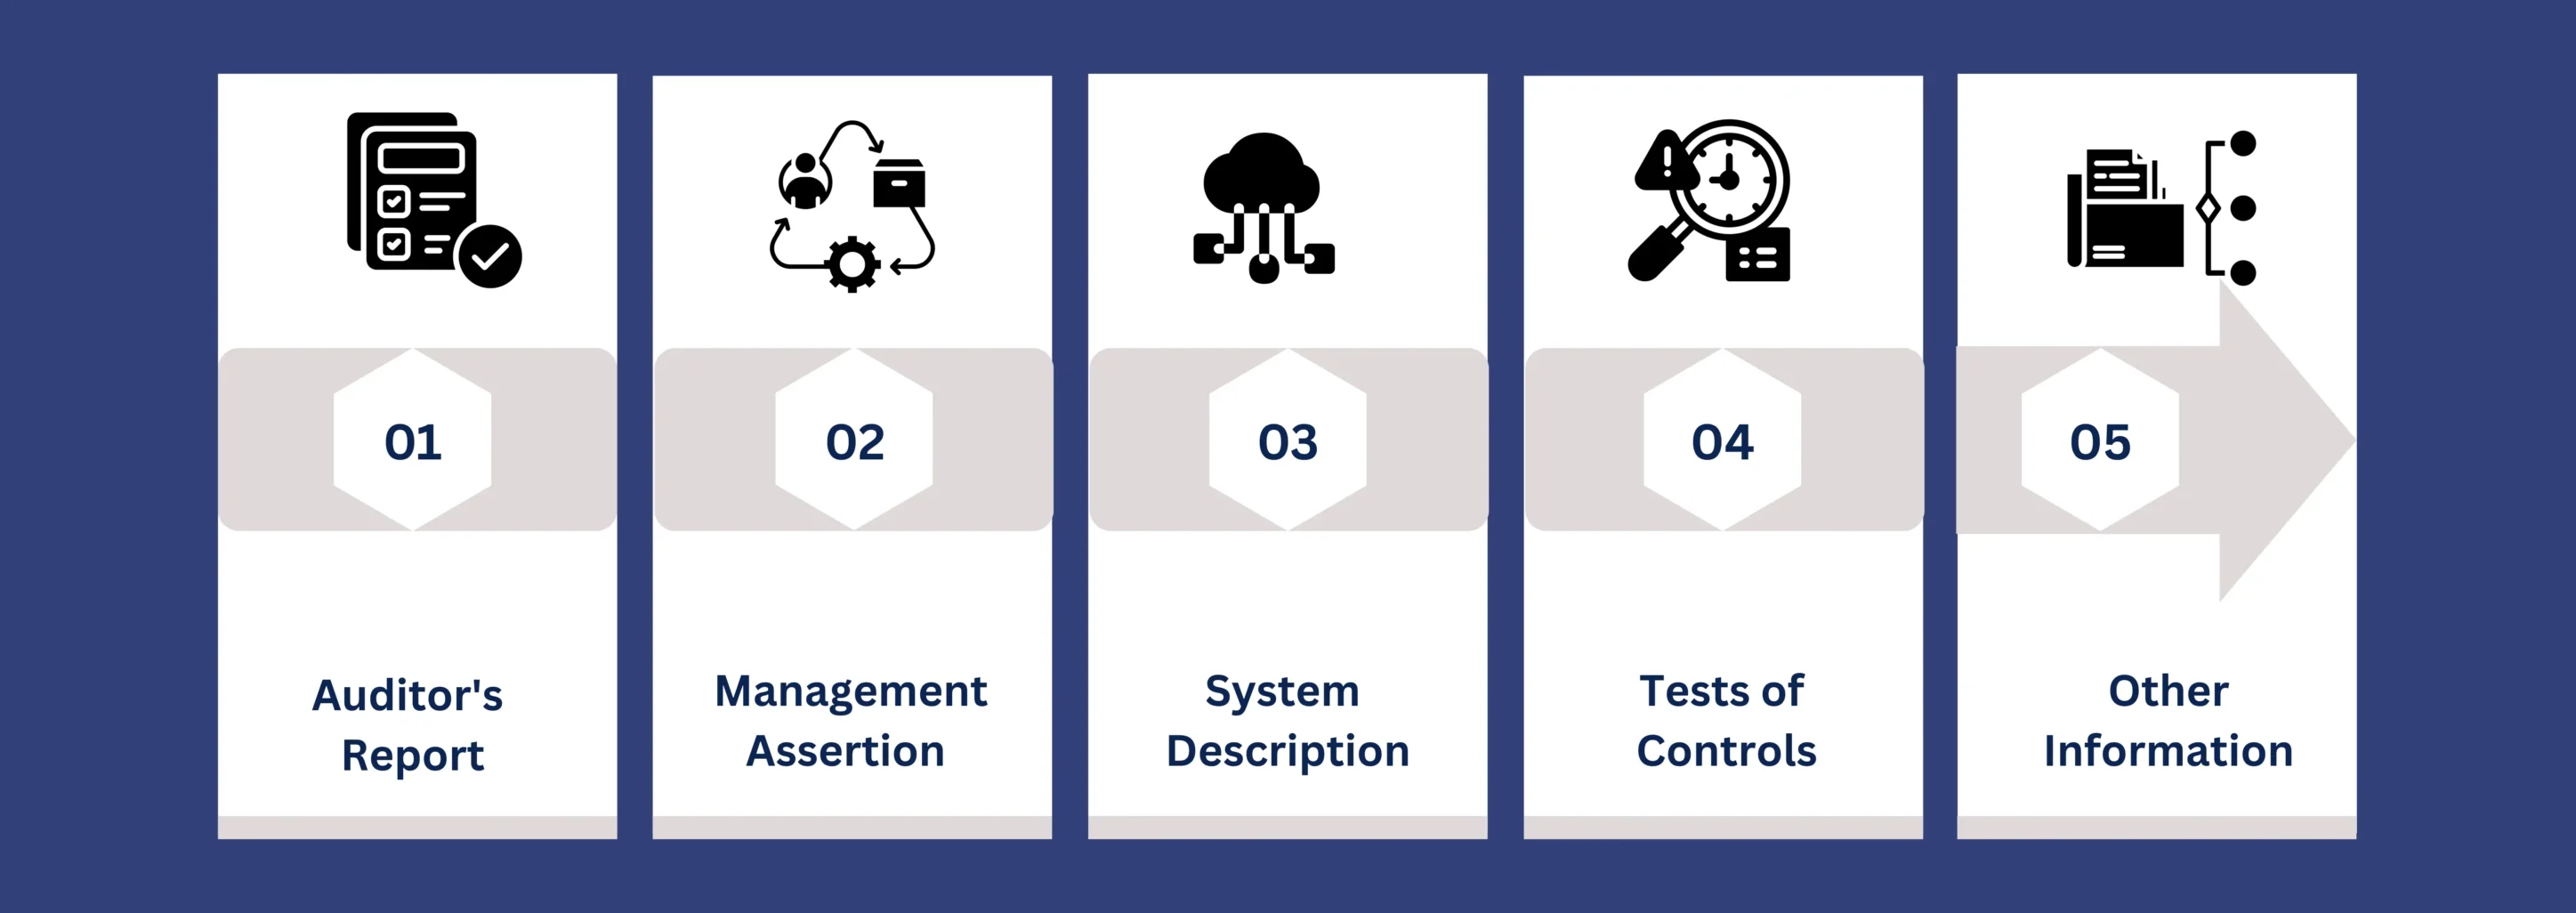
Sections of an Issued SOC 2 Report Explained
Understanding the anatomy of an actual SOC 2 report clarifies why its content cannot be templated. Every issued report follows a structure derived from AICPA guidance, but the substance within each section is engagement-specific (Source: AICPA Trust Services Criteria).
-
Section 1 — Auditor's Report
This is the CPA firm's formal opinion letter. It states the scope (which Trust Services Criteria were examined), the examination period, management's responsibility, the auditor's responsibility, and the opinion itself. The four possible opinions are: unqualified (controls meet criteria), qualified (controls substantially meet criteria with noted exceptions), adverse (controls do not meet criteria), or disclaimer (insufficient basis for an opinion). No template can produce this section — it is the CPA's professional conclusion.
-
Section 2 — Management Assertion
Management formally asserts that the system description is accurate and that controls were suitably designed and, for Type 2, operating effectively. This assertion creates the legal and professional framework between the service organization and the auditor.
-
Section 3 — System Description
A detailed narrative covering infrastructure, software, people, procedures, and data. Its length and complexity reflect the actual system examined — a SaaS platform with three microservices produces a materially different description than a multi-region cloud platform with dozens of integrations.
-
Section 4 — Tests of Controls
The longest section in any example SOC 2 report. For each control tested, the auditor documents the control description, the test procedures applied, and the results, including any exceptions noted. This section is examination-specific by definition.
-
Section 5 — Other Information
Optional management commentary, context, or responses to exceptions. Its presence and content vary by engagement.
Type 1 vs. Type 2: How the Report Structure Differs
An example SOC 2 report looks materially different depending on whether it is a Type 1 or Type 2 report, and understanding that difference helps organizations know what they are asking for when they seek an attestation.
A SOC 2 Type 1 report captures a single point in time. The auditor's opinion addresses whether controls were suitably designed as of a specified date. The tests of controls section documents design evaluation procedures — the auditor is not opining on whether controls actually operated over a period. Type 1 reports are typically shorter because the evidence population is limited to a single date.
A SOC 2 Type 2 report covers an examination period — typically six to twelve months. The auditor's opinion addresses both design suitability and operating effectiveness over that period. The tests of the controls section documents sample-based testing across the audit window, making this section significantly longer than its Type 1 equivalent. An example SOC 2 report for a Type 2 examination routinely exceeds 100 pages for organizations with moderate control environments (Source: AICPA).
This structural difference is why no single SOC 2 report template could serve both report types. A Type 2 report requires evidence of control operation across time — evidence that only exists after an examination period concludes. The report is built from that evidence; the evidence is not inserted into a pre-built report.
Bridge letters, sometimes requested when a report is approaching the end of its typical twelve-month useful life, are management-authored documents that provide interim assurance. They reference the previously issued report from the CPA firm and cannot substitute for a new examination.
-
Audit window
SOC 2 Type 1: Single specified date
SOC 2 Type 2: 3–12 month period -
Opinion covers
SOC 2 Type 1: Control design suitability
SOC 2 Type 2: Design suitability + operating effectiveness -
Tests of controls length
SOC 2 Type 1: Shorter — design evaluation only
SOC 2 Type 2: Longer — sample-based testing over the period -
Typical report length
SOC 2 Type 1: 30–60 pages
SOC 2 Type 2: 80–150+ pages -
Renewal cadence
SOC 2 Type 1: Upgrades to Type 2 as maturity grows
SOC 2 Type 2: Annual re-examination recommended
What CertPro Provides Instead of a Template
CertPro is a licensed CPA firm and independent attestation provider. When a technology organization engages CertPro for a SOC 2 examination, CertPro conducts the examination under AICPA AT-C standards and issues the formal attest report — the actual document that enterprise customers, procurement teams, and regulators require.
That issued report is not produced from a SOC 2 report template. It is the product of an independent examination: scoping the relevant Trust Services Criteria, evaluating the service organization's system description, testing controls against those criteria, and forming a professional opinion supported by documented evidence. The CPA firm's independence from the service organization is what gives the report its credibility and market acceptance.
For organizations trying to understand what a completed SOC 2 report looks like before engaging an auditor, published illustrative reports from the AICPA and annotated samples from educational sources are appropriate reference materials. Reviewing an example SOC 2 report helps management understand scope decisions, system description expectations, and the level of control documentation an auditor will examine. That preparation is valuable — but it is not the same as possessing an issued report.
CertPro performs independent SOC 2 examinations and issues applicable attest reports for technology companies seeking to demonstrate their security posture to customers and stakeholders. The report CertPro issues is the one your customers are asking for when they request a SOC 2 report download — not an illustrative PDF, but a signed opinion from an independent, licensed CPA firm.
Conclusion
The search for a SOC 2 report template reveals a genuine misunderstanding of what the document is and where it comes from. A SOC 2 report is a formal attest document produced by a licensed, independent CPA firm under AICPA professional standards. Its content — the auditor's opinion, the tests performed, the exceptions noted — is the direct output of an examination, not a form that can be downloaded, customized, and submitted.
Illustrative samples and example SOC 2 report PDFs serve a legitimate educational purpose: they help service organizations understand report structure, scope decisions, and what auditors examine. But no illustrative sample carries attestation value, and no SOC 2 report template can substitute for an issued report from an independent CPA.
CertPro, a licensed CPA firm, conducts SOC 2 examinations and issues the formal attest reports that technology organizations need to demonstrate their security posture to customers. That is what replaces the template: an independent examination and a professionally issued opinion that the market actually accepts.
Need an Issued SOC 2 Report, Not a Template?
CertPro is an independent, licensed CPA firm. We perform SOC 2 examinations under AICPA attestation standards and issue the formal attest report your customers ask for. Schedule a meeting with our auditors to discuss scope, examination period and evidence requirements.